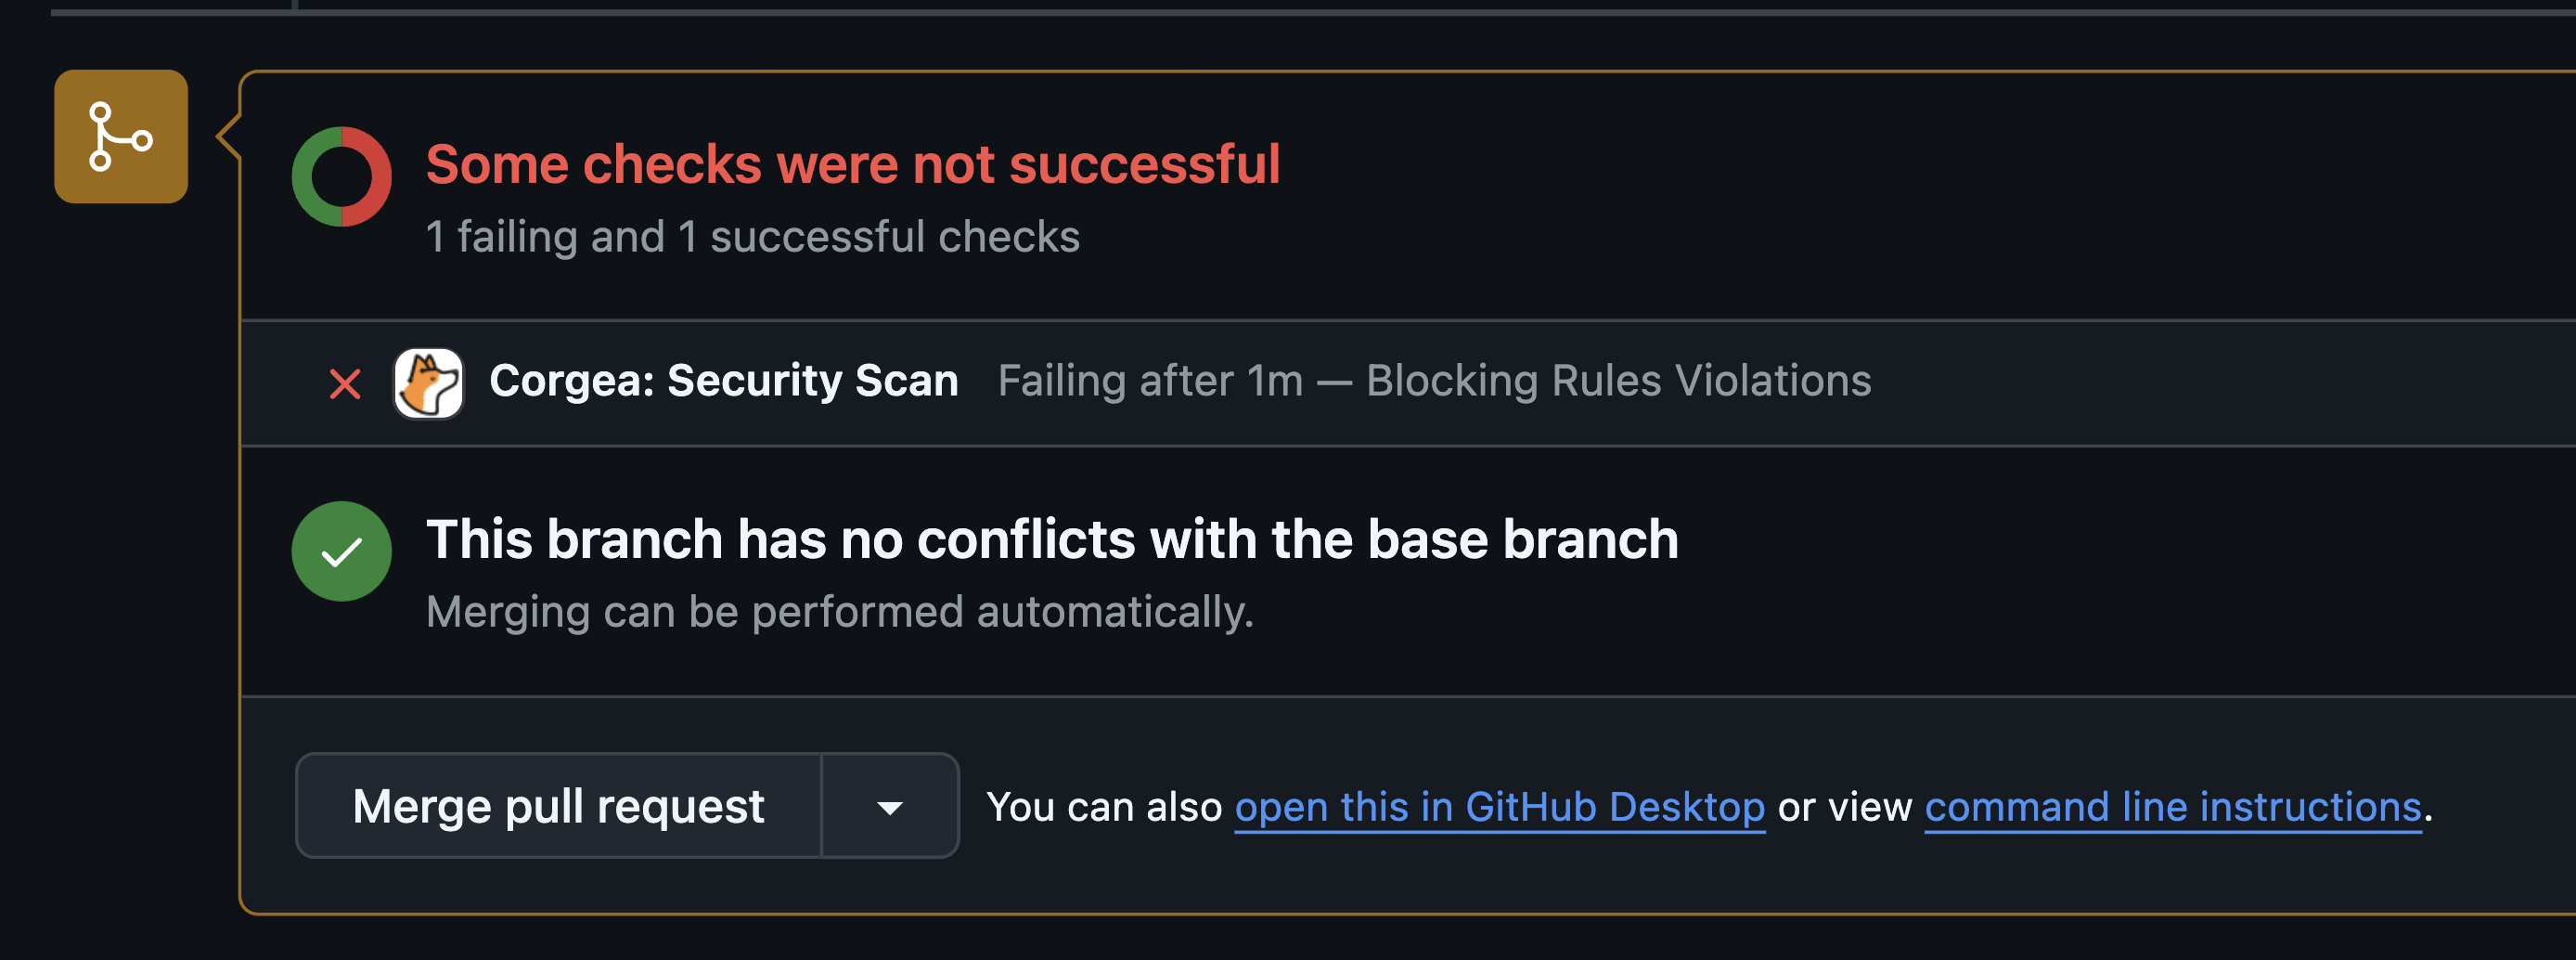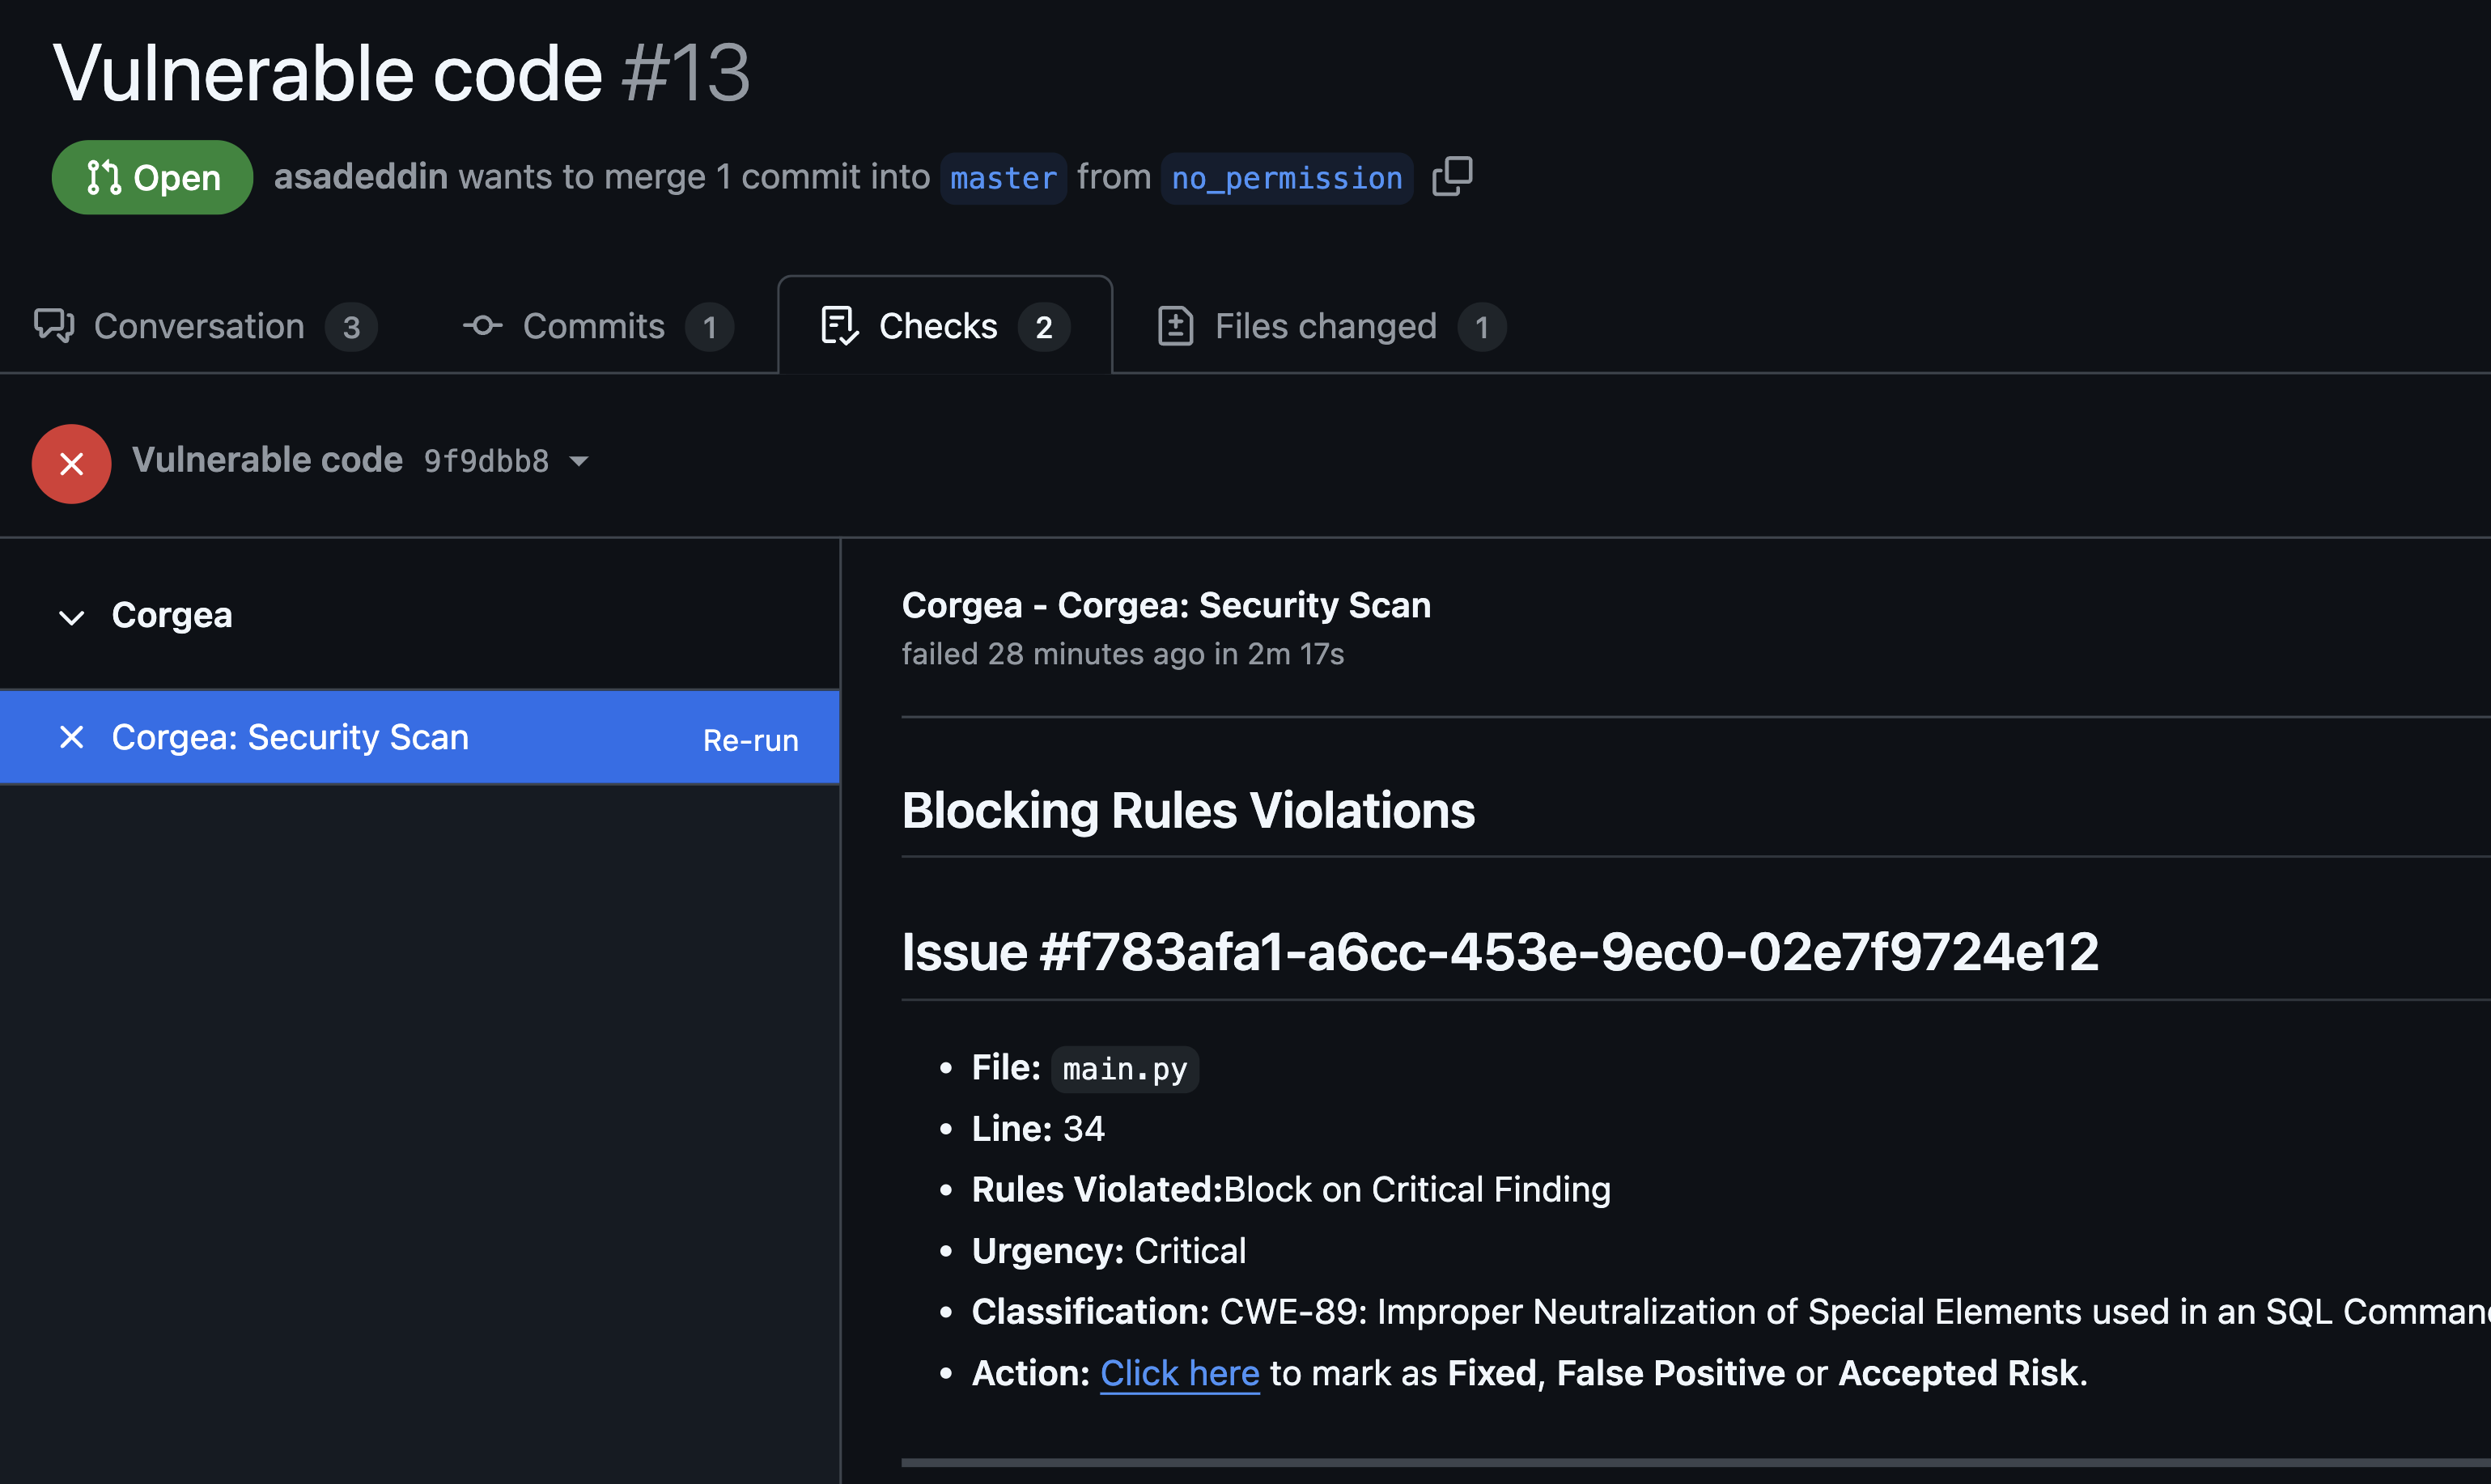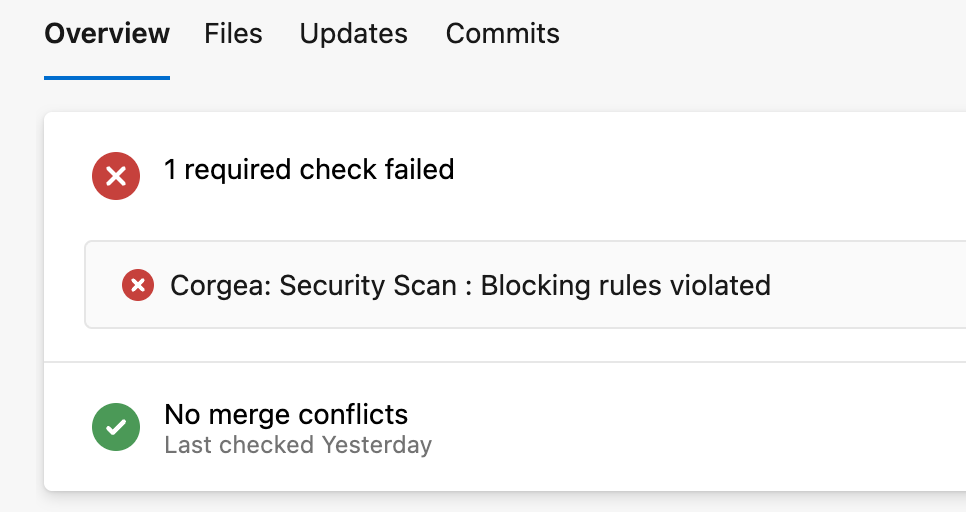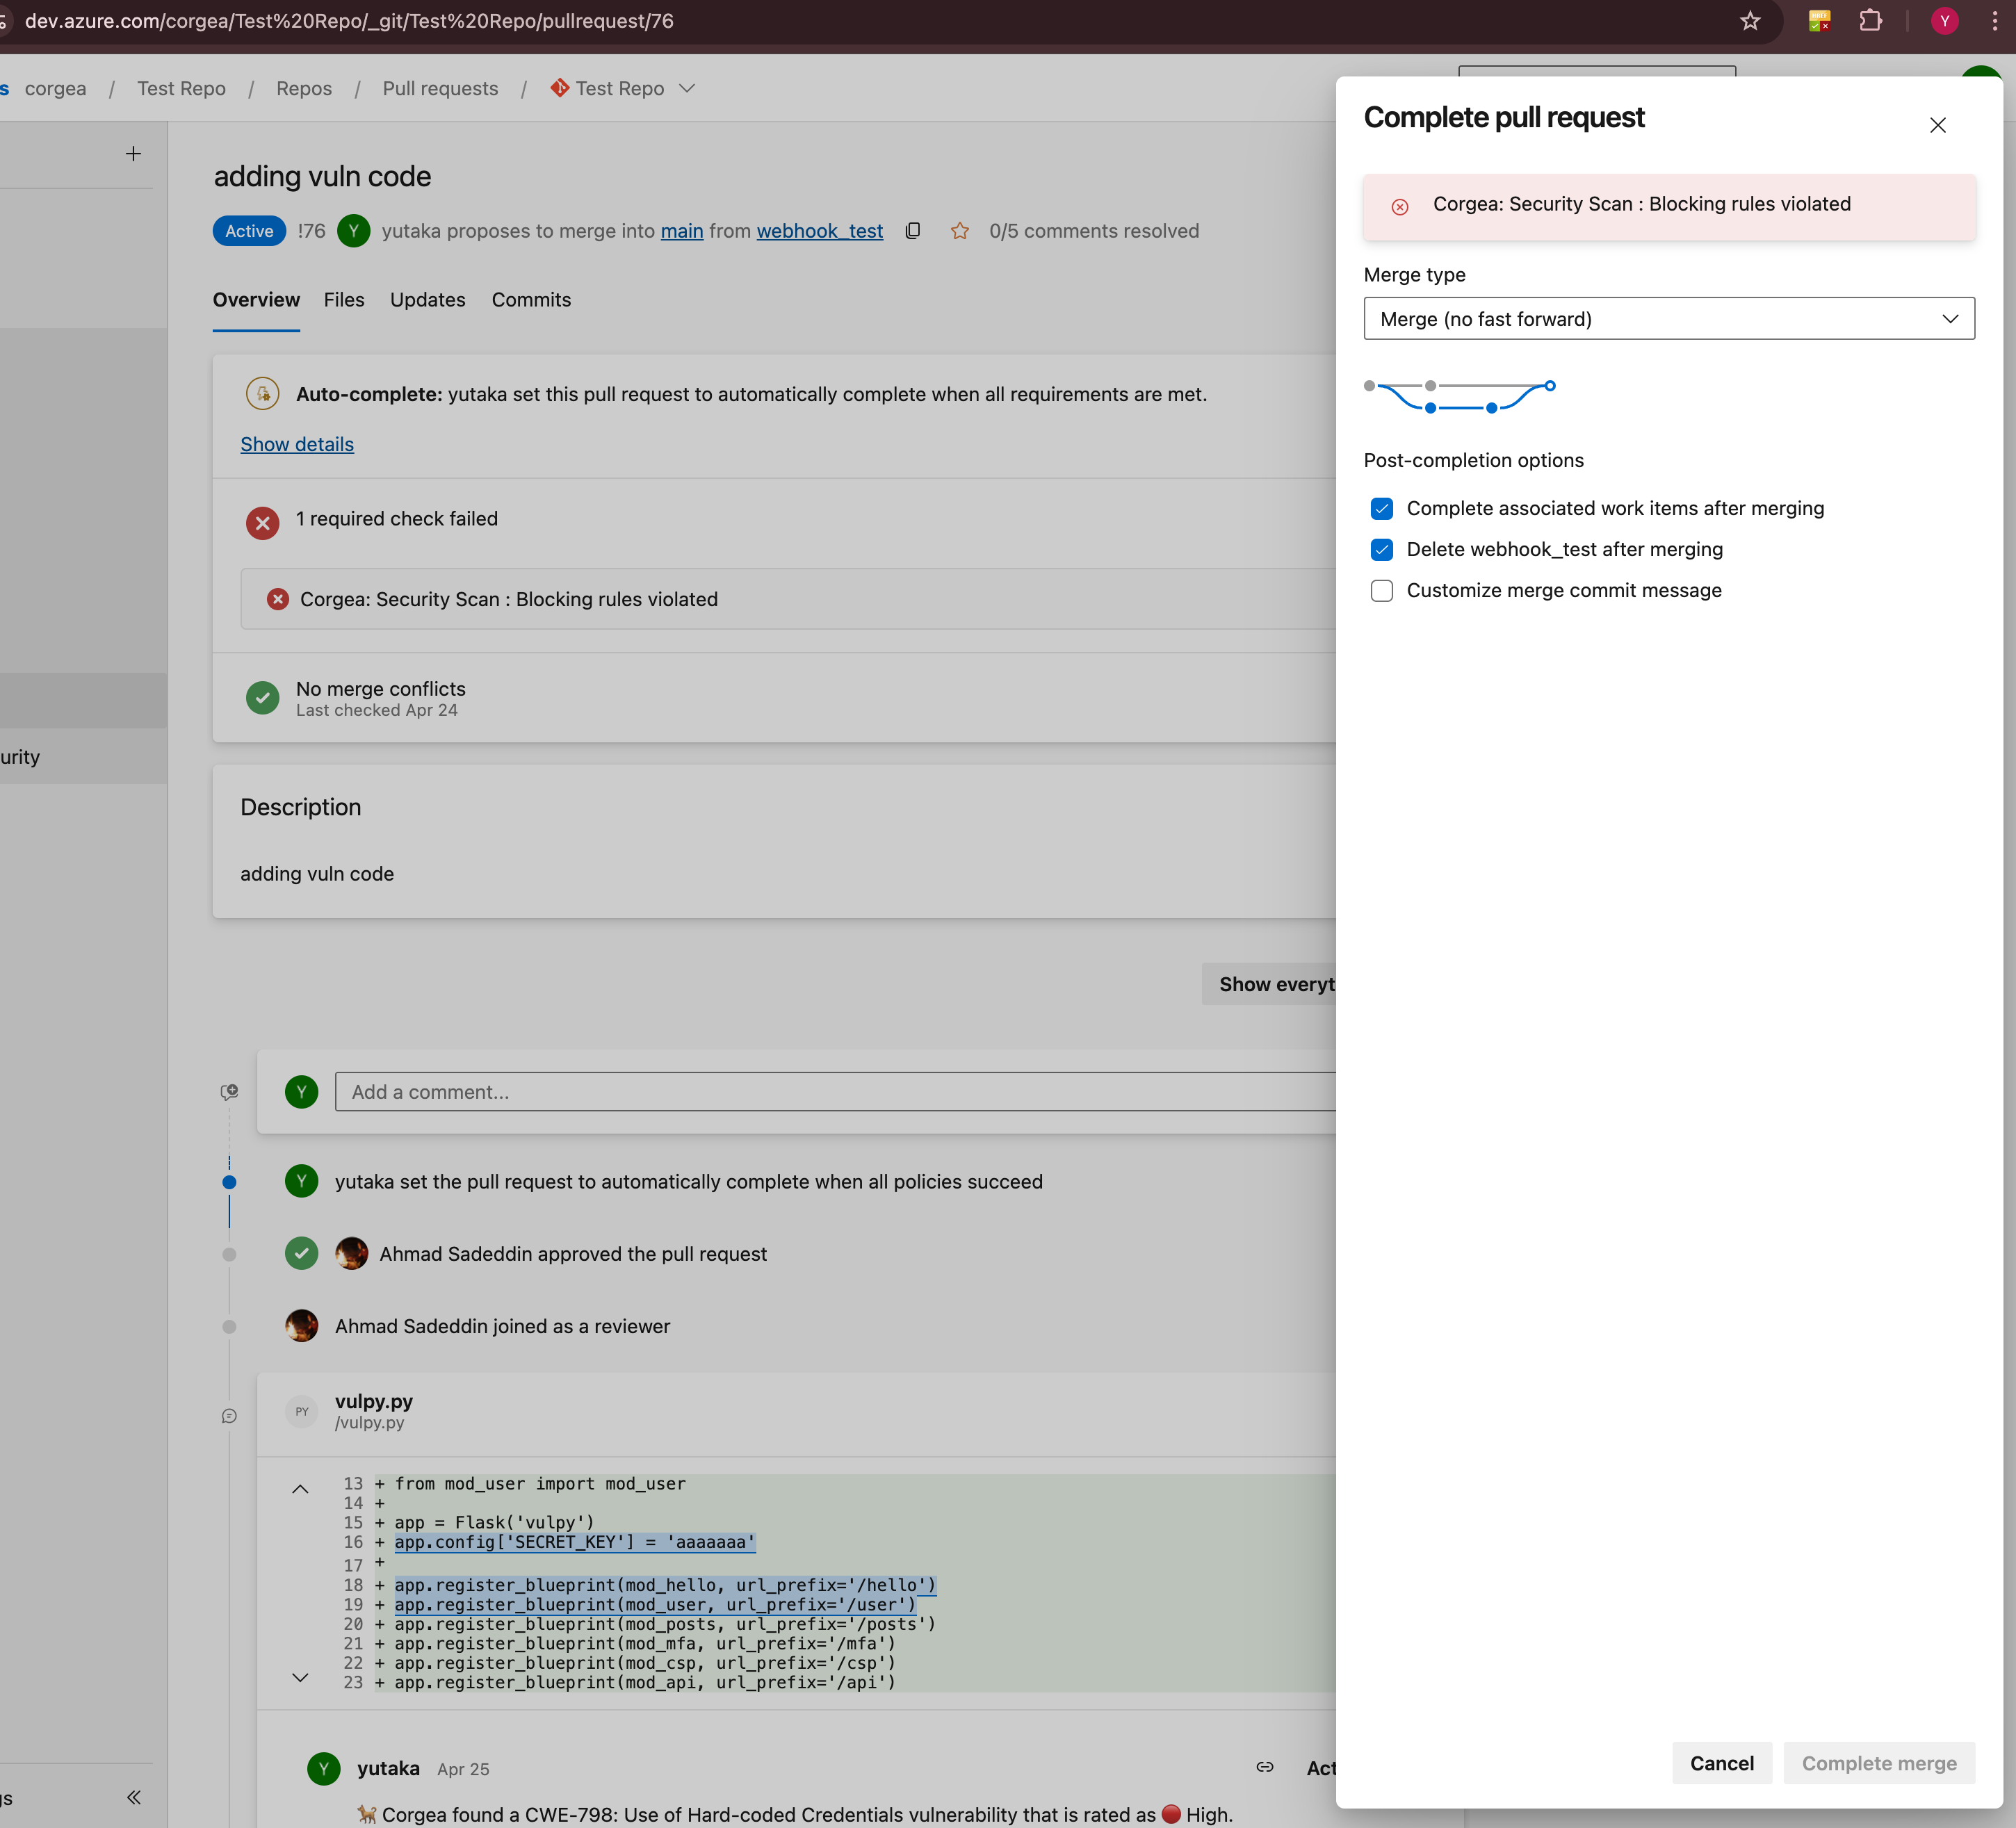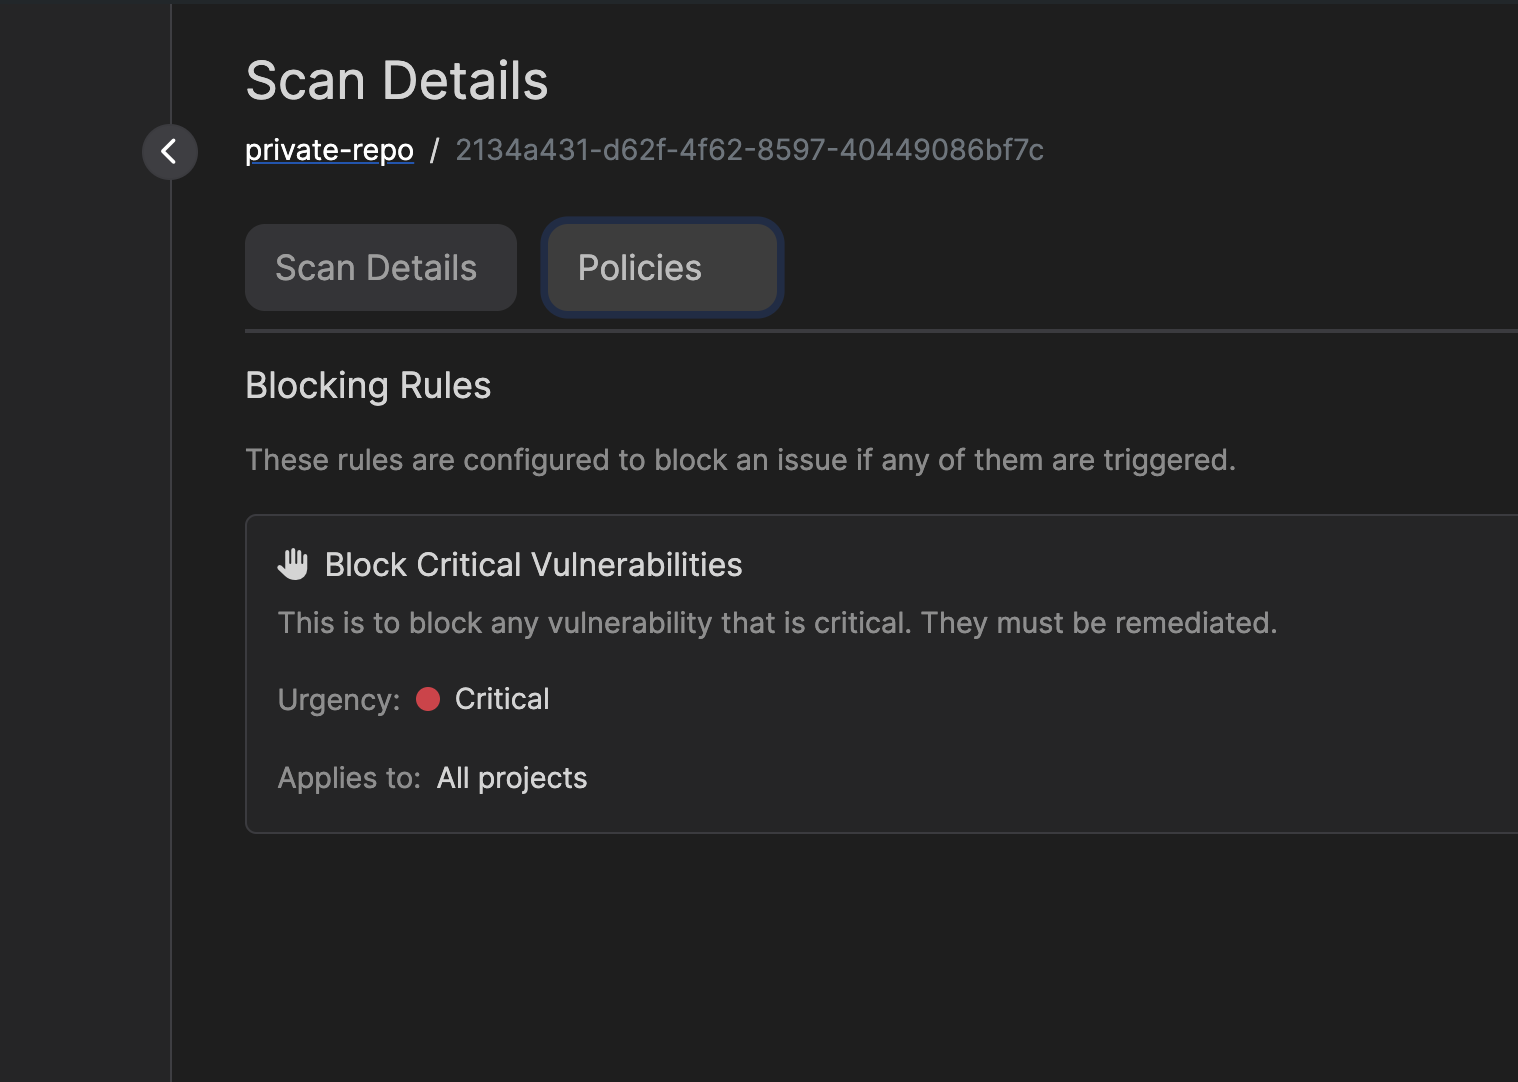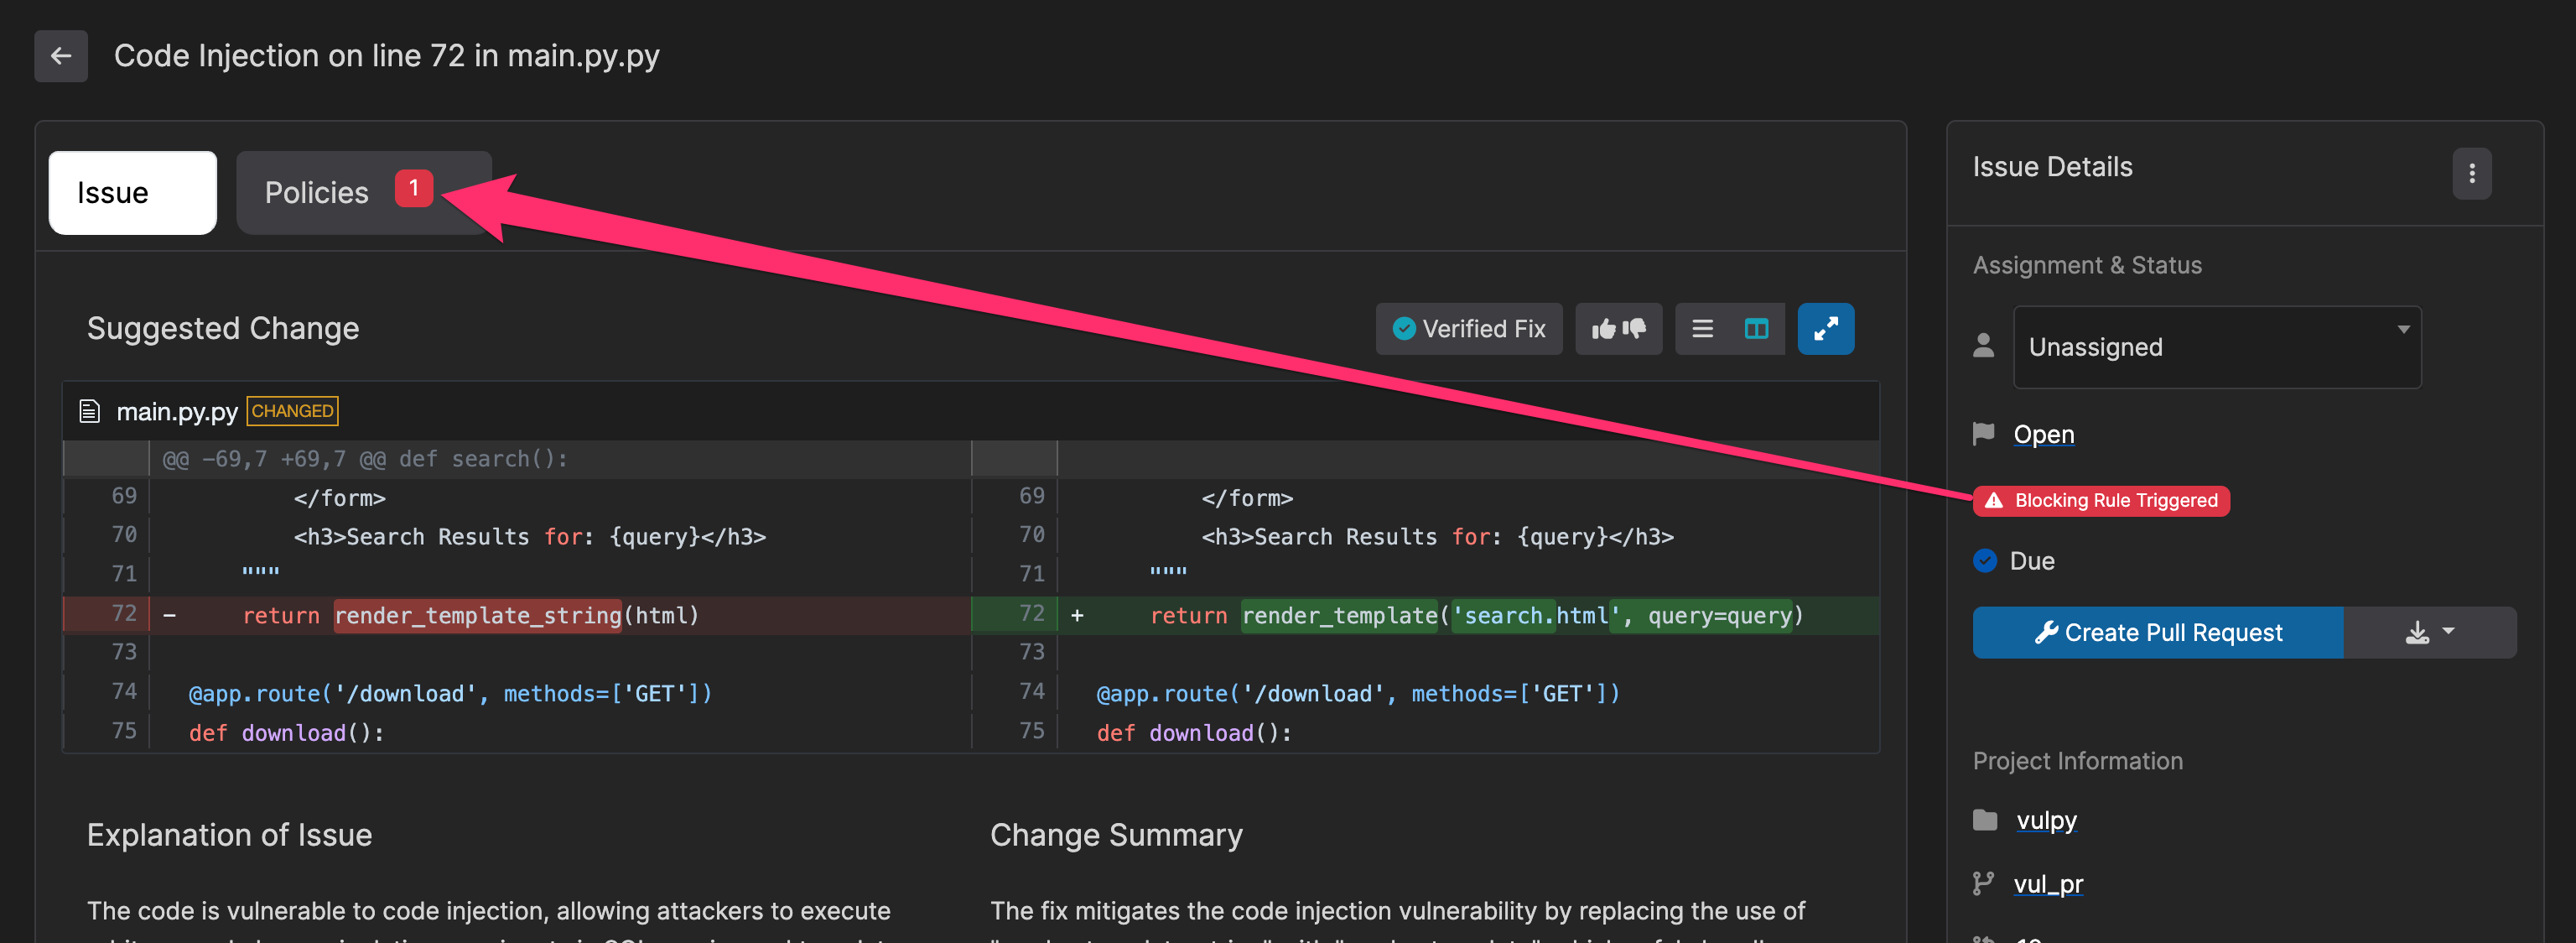
Blocking rules are guardrails that define which findings should fail a pull request check or CI pipeline. This helps ensure that your codebase adheres to your organization’s security and quality standards.You can create three types of blocking rules:
Code Vulnerability Rules: Block PRs based on security vulnerabilities, code-quality findings, or both
Dependency Vulnerability Rules: Block PRs based on vulnerable dependencies found by SCA scanning
License Compliance Rules: Block dependencies with specific SPDX licenses or license families
This feature is particularly useful for organizations with strict compliance requirements or those working on mission-critical applications where code quality and security are paramount.
Define rules based on Common Weakness Enumerations (CWEs) to block pull requests that introduce specific types of vulnerabilities or code quality issues.
Customize Urgency Levels
Assign urgency levels (e.g., critical, high, medium, low) to different types of issues, allowing you to prioritize and handle them accordingly.
Filter Dependencies by CVSS
For dependency vulnerability rules, define an inclusive CVSS score range to block vulnerable dependencies based on their CVSS score.
Filter Dependencies by Reachability
For dependency vulnerability rules that apply to CI, narrow blocking to dependencies whose vulnerable code is actually reachable from your application, so unused and unreachable packages do not fail your pipeline.
Enforce License Policy
Block dependencies by specific SPDX license IDs or by the Copyleft, Permissive, and Commercial license families.
Project and Tag Scoped Rules
Apply blocking rules to specific projects, project tags, or across your entire organization, giving you granular control over which projects are subject to which rules.
Rule Management
Easily create, edit, and delete blocking rules through a user-friendly interface, ensuring your rules stay up-to-date with your evolving requirements.
Rule Activation/Deactivation
Toggle the status of blocking rules to temporarily enable or disable them as needed, without losing their configurations.
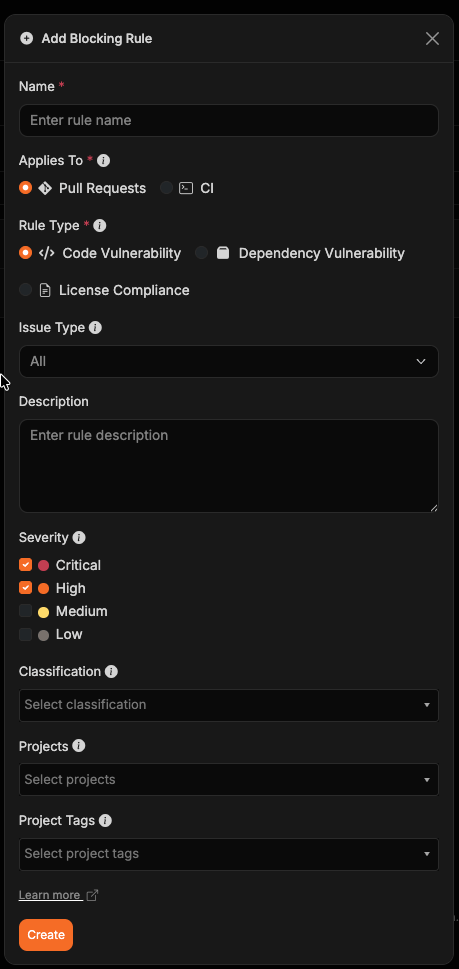
Code Vulnerability: Block pull requests based on code security issues (SAST findings)
Dependency Vulnerability: Block pull requests based on vulnerable dependencies (SCA findings)
License Compliance: Block dependencies based on denied SPDX licenses or license families
3
Basic Information
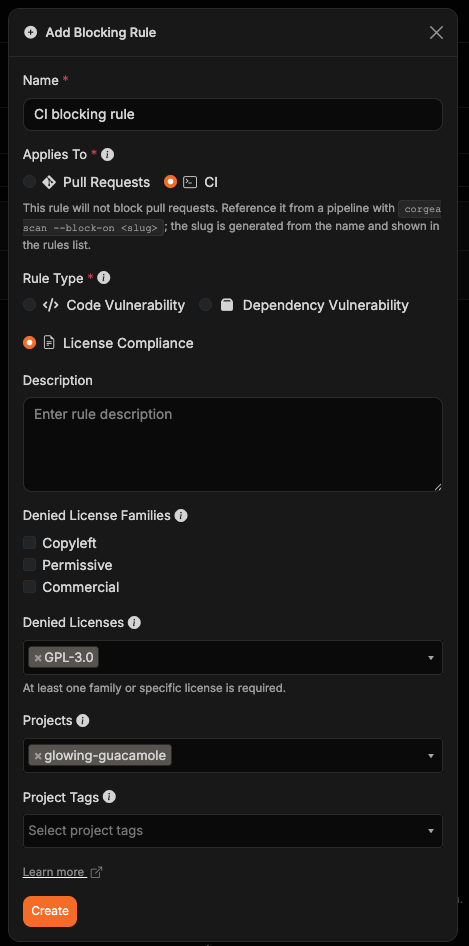
Enter the rule name and description, then choose Applies To:
Pull Requests automatically enforces the rule in pull request checks.
CI enforces the rule only when a pipeline names it with corgea scan --block-on <slug>. CI rules do not block pull requests.
New rules default to Pull Requests. Corgea generates the slug from the rule name and displays it in the rules list.Pull request rules only comment on actionable findings. Corgea skips comments for findings confirmed as unreachable, findings held because they are false positives or unsupported-language results, and findings in paths ignored by the project. These findings remain available in Corgea for review, but they do not block the pull request.
4
Configure Settings
For Code Vulnerability rules: Choose an Issue Type to apply the rule to All findings, Vulnerabilities only, or Code Quality findings only. All is the default and preserves the behavior of existing rules. Then select urgency levels (Critical, High, Medium, or Low) and/or target CWEs; at least one of these must be defined for the rule to be valid.For Dependency Vulnerability rules: Choose whether to filter by severity or CVSS score. Select urgency levels (Critical, High, Medium, or Low), or enter a minimum and maximum CVSS score from 0.0 to 10.0 to block vulnerable dependencies within that inclusive range. If the rule applies to CI, you can also select one or more Reachability states to narrow it further — see Filtering by Reachability.For License Compliance rules: Select at least one denied license family (Copyleft, Permissive, or Commercial) or enter one or more SPDX license IDs. A dependency is blocked when any reported license matches a selected family or specific ID.
5
Set Scope
Choose applicable projects and/or project tags (optional). A rule applies when a project is selected directly or has any selected tag. If no projects or tags are selected, the rule applies to all projects.
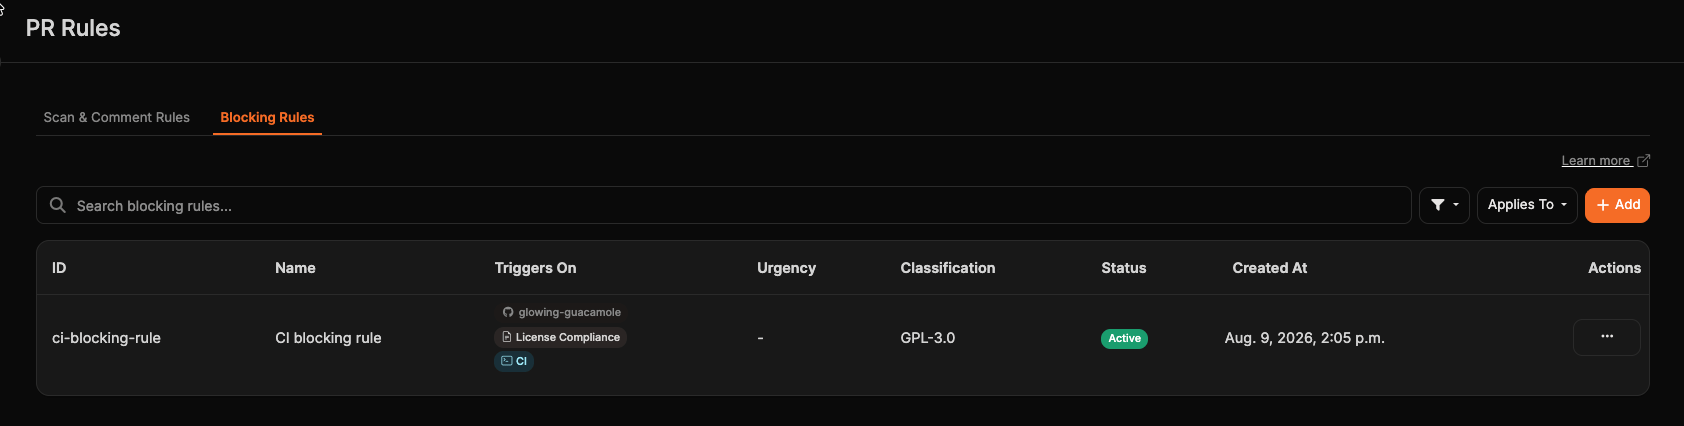
Use search to find rules by name or settings, or filter the list by project tag or Applies To target. The rules table shows each rule’s slug in the ID column and surfaces the project scope, rule type, and Pull Requests or CI target under Triggers On. Select a slug to copy it for use in a CI command. Rules without a project or tag scope apply to all projects, and longer scope lists are grouped behind a +N more tooltip.
Create an active rule with Applies To set to CI, then pass its slug to the scan command. Name rules for the condition that trips them — for example criticals, not no-criticals — so --block-on reads as a direct assertion. --block-on requires Corgea CLI 1.10.0 or later.
corgea scan --block-on criticals
To enforce multiple CI rules, provide their slugs as a comma-separated list. The command fails when a finding violates any named rule. An unknown slug, inactive rule, or rule that applies to pull requests is treated as a configuration error rather than being skipped. --block-on is supported only by the BLAST scanner and cannot be combined with --fail or --fail-on.
Most vulnerable dependencies in a project are never actually exercised by your code. Reachability filtering lets a Dependency Vulnerability rule block only the findings that matter, so a critical CVE in a package you never call does not fail your pipeline.
Available for CI rules only Reachability is analyzed on scans you start yourself with corgea scan, not on the scans triggered automatically when a pull request opens. Set Applies To to CI to use this filter; the option is hidden for Pull Request rules, and reference the rule from your pipeline with corgea scan --block-on <slug>.
Prerequisite Reachability requires AI-Native SCA to be enabled for your organization. Without it no dependency is analyzed, so a rule using this filter never blocks anything. The rule editor warns you when the setting is off.
Select one or more of the following states:
State
Meaning
Reachable
The vulnerable function is reachable from your application code.
Not Reachable
The dependency is used, but the vulnerable function is not reachable.
Unused Dependency
The dependency is declared but not used anywhere in the codebase.
Unknown
The dependency was analyzed but reachability could not be determined.
The reachability filter is combined with the severity, CVSS, or Malicious filter rather than replacing it, so a finding must match both. A rule set to Critical severity and Reachable blocks only critical vulnerabilities that are also reachable. Leaving reachability empty keeps the rule’s existing behavior of blocking regardless of reachability.
Reachability analysis runs after the scan itself completes, so corgea scan keeps polling while it finishes rather than reporting a result immediately. Analysis is done once every direct dependency has been analyzed, typically a few minutes and at most 30.This filter fails open. If analysis cannot finish — the 30-minute window elapses, analysis fails, or AI-Native SCA is disabled — the rule reports no violation instead of failing your build. A pipeline is only ever blocked on reachability that Corgea actually determined, never on missing analysis.
corgea scan fails closed on its own deadline. Corgea CLI 1.13.0 and later allow 35 minutes, comfortably outlasting the 30-minute analysis window. On an earlier CLI the deadline is 15 minutes, which can expire while Corgea is still analyzing and fail the pipeline. Either upgrade the CLI or raise the deadline with CORGEA_BLOCKING_RULES_TIMEOUT_SECONDS:
Rule Type: Code VulnerabilityCreate a rule targeting CWE-326 (Inadequate Encryption Strength) and CWE-327 (Use of a Broken or Risky Cryptographic Algorithm) with “Critical” urgency to prevent weak encryption usage.
Enforcing Code Quality
Rule Type: Code VulnerabilitySelect Code Quality as the issue type, then set up a rule for CWE-398 (Indicator of Poor Code Quality) and CWE-477 (Use of Obsolete Functions) with “Medium” urgency to maintain code standards.
Blocking Critical Dependency Vulnerabilities
Rule Type: Dependency VulnerabilityCreate a rule with “Critical” and “High” urgency levels selected to automatically block any pull request that introduces dependencies with critical or high-severity vulnerabilities. This ensures your supply chain remains secure and prevents known vulnerable packages from entering your codebase.
Blocking Dependencies by CVSS Range
Rule Type: Dependency VulnerabilityCreate a rule that filters by CVSS score, such as 7.0 to 10.0, to block pull requests that introduce vulnerable dependencies within that score range.
Blocking Only Reachable Critical Vulnerabilities
Rule Type: Dependency Vulnerability — Applies To: CISelect “Critical” and “High” urgency levels, then select Reachable under Reachability. The rule fails a pipeline only when a critical or high-severity vulnerability is reachable from your application code, so unused and unreachable packages do not interrupt developers. This is a good first reachability rule because it narrows an existing severity rule rather than widening what blocks.
Blocking Unused Dependencies
Rule Type: Dependency Vulnerability — Applies To: CISelect Unused Dependency under Reachability on its own, with no severity or CVSS filter. The rule fails a pipeline that introduces vulnerable packages nothing in the codebase uses, prompting developers to remove the dependency instead of upgrading it.
Blocking Copyleft Dependencies
Rule Type: License ComplianceSelect the Copyleft family to block dependencies whose reported licenses belong to that family. Add specific SPDX IDs when your policy needs a narrower denylist.
For Dependency Vulnerability rules, begin with Critical severity only or a focused CVSS range, then expand as your team adjusts
On CI rules, add a Reachable reachability filter to an existing severity rule to cut noise without weakening coverage of the vulnerabilities that are actually exploitable
For Code Vulnerability rules, focus on the most impactful CWEs first (e.g., injection flaws, authentication issues)
Regular review and updates
Clear documentation and team training
Encourage feedback and collaboration
Strategic use of urgency levels
Consider project tags when the same rule should cover a group of related projects
If a pull request is unexpectedly blocked, verify the active rules and their configurations first.
Common Issues
Unexpected blocking behavior
Rule targeting issues
Project scope problems
Resolution Steps
Check rule configurations
Verify CWE targeting
Confirm project settings
Contact support if needed
Was this page helpful?
{"docsConfig":{"theme":"palm","$schema":"https://mintlify.com/docs.json","name":"Corgea Documentation","colors":{"primary":"#F56C26","light":"#F56C26","dark":"#F56C26"},"logo":{"light":"https://mintcdn.com/corgea/mpJUc1GyXtnVYEyT/logo/logo.png?fit=max\u0026auto=format\u0026n=mpJUc1GyXtnVYEyT\u0026q=85\u0026s=f66a9484335ac4db5d5d92e12fd87af6","dark":"https://mintcdn.com/corgea/mpJUc1GyXtnVYEyT/logo/logo.png?fit=max\u0026auto=format\u0026n=mpJUc1GyXtnVYEyT\u0026q=85\u0026s=f66a9484335ac4db5d5d92e12fd87af6"},"favicon":"https://mintcdn.com/corgea/mpJUc1GyXtnVYEyT/logo/logo.png?fit=max\u0026auto=format\u0026n=mpJUc1GyXtnVYEyT\u0026q=85\u0026s=f66a9484335ac4db5d5d92e12fd87af6","background":{"color":{"light":"#fffdfd","dark":"#131313"}},"navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Support"}],"primary":{"type":"button","label":"Go to Corgea","href":"https://www.corgea.app"}},"footer":{"socials":{"twitter":"https://x.com/CorgeaInc","github":"https://github.com/Corgea","linkedin":"https://www.linkedin.com/company/corgea"}},"integrations":{"ga4":{"measurementId":"G-GGF9NXG1LJ"}},"styling":{"latex":false},"navigation":{"languages":[{"language":"en","default":true,"navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Support"}],"primary":{"type":"button","label":"Go to Corgea","href":"https://www.corgea.app"}},"href":"introduction"},{"language":"de","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Support"}],"primary":{"type":"button","label":"Zu Corgea","href":"https://www.corgea.app"}},"href":"de/introduction"},{"language":"fr","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Assistance"}],"primary":{"type":"button","label":"Accéder à Corgea","href":"https://www.corgea.app"}},"href":"fr/introduction"},{"language":"es","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Soporte"}],"primary":{"type":"button","label":"Ir a Corgea","href":"https://www.corgea.app"}},"href":"es/introduction"},{"language":"ja","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"サポート"}],"primary":{"type":"button","label":"Corgeaを開く","href":"https://www.corgea.app"}},"href":"ja/introduction"}]}},"deployment":{"deploymentMetadataValue":{"subdomain":"corgea","hasAudioNarration":false,"actualSubdomain":"corgea","customDomains":["docs.corgea.app"],"gitSource":{"type":"github","owner":"corgea","repo":"docs","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"chroma":{"liveDeploymentHistoryId":"6ae550291d528968cec4ede6","collectionId":"fa225268-b341-4285-9fb7-c791f78b926b","schemaVersion":"v3","latestBuiltDeploymentHistoryId":"6ae550291d528968cec4ede6"},"feedback":{"thumbs":true},"entitlements":{},"buildId":"6ae550291d528968cec4ede6","clientVersion":"0.0.4044","searchFilterCounts":[{"language":"en","tag":"API Reference","count":83},{"language":"de","tag":"API-Referenz","count":83},{"language":"es","tag":"Referencia de la API","count":83},{"language":"fr","tag":"Référence API","count":83},{"language":"ja","tag":"APIリファレンス","count":80},{"language":"en","tag":"Documentation","count":57},{"language":"de","tag":"Dokumentation","count":55},{"language":"es","tag":"Documentación","count":55},{"language":"fr","tag":"Documentation","count":55},{"language":"ja","tag":"ドキュメント","count":55},{"language":"en","tag":"Core Features","count":30},{"language":"de","tag":"Kernfunktionen","count":30},{"language":"es","tag":"Funciones principales","count":30},{"language":"fr","tag":"Fonctionnalités principales","count":30},{"language":"ja","tag":"主な機能","count":30},{"language":"en","tag":"Issues","count":16},{"language":"de","tag":"Issues","count":16},{"language":"es","tag":"Hallazgos","count":16},{"language":"fr","tag":"Problèmes","count":16},{"language":"ja","tag":"問題","count":16},{"language":"en","tag":"Integrations","count":15},{"language":"de","tag":"Integrationen","count":15},{"language":"es","tag":"Integraciones","count":15},{"language":"fr","tag":"Intégrations","count":15},{"language":"ja","tag":"インテグレーション","count":15},{"language":"en","tag":"Security Scanning","count":10},{"language":"de","tag":"Sicherheitsscans","count":10},{"language":"es","tag":"Análisis de seguridad","count":10},{"language":"fr","tag":"Analyse de sécurité","count":10},{"language":"ja","tag":"セキュリティスキャン","count":10},{"language":"en","tag":"Authentication","count":8},{"language":"en","tag":"Teams","count":8},{"language":"de","tag":"Authentifizierung","count":8},{"language":"de","tag":"Teams","count":8},{"language":"es","tag":"Autenticación","count":8},{"language":"es","tag":"Equipos","count":8},{"language":"fr","tag":"Authentification","count":8},{"language":"fr","tag":"Équipes","count":8},{"language":"ja","tag":"認証","count":8},{"language":"ja","tag":"チーム","count":8},{"language":"en","tag":"Issue Management","count":7},{"language":"en","tag":"Notifications","count":7},{"language":"de","tag":"Issue-Management","count":7},{"language":"de","tag":"Benachrichtigungen","count":7},{"language":"es","tag":"Gestión de hallazgos","count":7},{"language":"es","tag":"Notificaciones","count":7},{"language":"fr","tag":"Gestion des résultats","count":7},{"language":"fr","tag":"Notifications","count":7},{"language":"ja","tag":"検出結果の管理","count":7},{"language":"ja","tag":"通知","count":7}]},"assistantConfig":{},"basePath":"","hasChatPermissions":false,"hasWebMcpPermissions":false,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"byok-sep-25","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"vite-origin","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-updated-9-15","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[],"page":{"pagePath":"blocking_rules","slug":"/blocking_rules","pageMetadata":{"title":"Blocking Rules","description":"Blocking rules enforce security and quality standards in pull requests or CI pipelines.","href":"/blocking_rules"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Blocking rules enforce security and quality standards in pull requests or CI pipelines.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,code:`code`,li:`li`,ol:`ol`,p:`p`,pre:`pre`,span:`span`,strong:`strong`,tbody:`tbody`,td:`td`,th:`th`,thead:`thead`,tr:`tr`,ul:`ul`,..._provideComponents(),...props.components},{Accordion,AccordionGroup,Card,CardGroup,CodeBlock,Frame,Heading,Info,OptimizedImage,Step,Steps,Tab,Table,Tabs,Warning}=_components;if(!Accordion)_missingMdxReference(`Accordion`,true);if(!AccordionGroup)_missingMdxReference(`AccordionGroup`,true);if(!Card)_missingMdxReference(`Card`,true);if(!CardGroup)_missingMdxReference(`CardGroup`,true);if(!CodeBlock)_missingMdxReference(`CodeBlock`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Info)_missingMdxReference(`Info`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Tab)_missingMdxReference(`Tab`,true);if(!Table)_missingMdxReference(`Table`,true);if(!Tabs)_missingMdxReference(`Tabs`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsx(Heading,{level:`2`,id:`overview`,children:`Overview`}),`\n`,_jsx(Heading,{level:`3`,id:`what-it-does`,children:`What it Does`}),`\n`,_jsx(_components.p,{children:`Blocking rules are guardrails that define which findings should fail a pull request check or CI pipeline. This helps ensure that your codebase adheres to your organization’s security and quality standards.`}),`\n`,_jsx(_components.p,{children:`You can create three types of blocking rules:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Code Vulnerability Rules`}),`: Block PRs based on security vulnerabilities, code-quality findings, or both`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Dependency Vulnerability Rules`}),`: Block PRs based on vulnerable dependencies found by SCA scanning`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`License Compliance Rules`}),`: Block dependencies with specific SPDX licenses or license families`]}),`\n`]}),`\n`,_jsx(Heading,{level:`3`,id:`who-it’s-for`,children:`Who it’s For`}),`\n`,_jsx(_components.p,{children:`Blocking rules are primarily designed for:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Development teams`}),`\n`,_jsx(_components.li,{children:`Project managers`}),`\n`,_jsx(_components.li,{children:`Security professionals`}),`\n`]}),`\n`,_jsx(_components.p,{children:`This feature is particularly useful for organizations with strict compliance requirements or those working on mission-critical applications where code quality and security are paramount.`}),`\n`,_jsx(Heading,{level:`2`,id:`key-features-and-benefits`,children:`Key Features and Benefits`}),`\n`,_jsxs(AccordionGroup,{children:[_jsx(Accordion,{title:`Enforce Coding Standards`,icon:`shield-check`,id:`enforce-coding-standards`,children:_jsx(_components.p,{children:`Define rules based on Common Weakness Enumerations (CWEs) to block pull requests that introduce specific types of vulnerabilities or code quality issues.`})}),_jsx(Accordion,{title:`Customize Urgency Levels`,icon:`signal`,id:`customize-urgency-levels`,children:_jsx(_components.p,{children:`Assign urgency levels (e.g., critical, high, medium, low) to different types of issues, allowing you to prioritize and handle them accordingly.`})}),_jsx(Accordion,{title:`Filter Dependencies by CVSS`,icon:`gauge`,id:`filter-dependencies-by-cvss`,children:_jsx(_components.p,{children:`For dependency vulnerability rules, define an inclusive CVSS score range to block vulnerable dependencies based on their CVSS score.`})}),_jsx(Accordion,{title:`Filter Dependencies by Reachability`,icon:`diagram-project`,id:`filter-dependencies-by-reachability`,children:_jsx(_components.p,{children:`For dependency vulnerability rules that apply to CI, narrow blocking to dependencies whose vulnerable code is actually reachable from your application, so unused and unreachable packages do not fail your pipeline.`})}),_jsx(Accordion,{title:`Enforce License Policy`,icon:`file-contract`,id:`enforce-license-policy`,children:_jsx(_components.p,{children:`Block dependencies by specific SPDX license IDs or by the Copyleft, Permissive, and Commercial license families.`})}),_jsx(Accordion,{title:`Project and Tag Scoped Rules`,icon:`folder-tree`,id:`project-and-tag-scoped-rules`,children:_jsx(_components.p,{children:`Apply blocking rules to specific projects, project tags, or across your entire organization, giving you granular control over which projects are subject to which rules.`})}),_jsx(Accordion,{title:`Rule Management`,icon:`gear`,id:`rule-management`,children:_jsx(_components.p,{children:`Easily create, edit, and delete blocking rules through a user-friendly interface, ensuring your rules stay up-to-date with your evolving requirements.`})}),_jsx(Accordion,{title:`Rule Activation/Deactivation`,icon:`toggle-on`,id:`rule-activation-deactivation`,children:_jsx(_components.p,{children:`Toggle the status of blocking rules to temporarily enable or disable them as needed, without losing their configurations.`})})]}),`\n`,_jsx(Heading,{level:`2`,id:`rule-types`,children:`Rule Types`}),`\n`,_jsx(_components.p,{children:`Blocking rules support three distinct types to provide comprehensive security coverage:`}),`\n`,_jsxs(CardGroup,{cols:3,children:[_jsxs(Card,{title:`Code Vulnerability`,icon:`code`,children:[_jsxs(_components.p,{children:[`Blocks pull requests based on `,_jsx(_components.strong,{children:`security vulnerabilities`}),`, `,_jsx(_components.strong,{children:`code-quality findings`}),`, or both.`]}),_jsx(_components.p,{children:`Configure by:`}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Selecting an issue type: All, Vulnerabilities, or Code Quality`}),`\n`,_jsx(_components.li,{children:`Selecting specific CWE (Common Weakness Enumeration) categories`}),`\n`,_jsx(_components.li,{children:`Setting urgency/severity levels`}),`\n`]}),_jsx(_components.p,{children:`Use this to prevent issues like SQL injection, XSS, insecure cryptography, and other code-level vulnerabilities.`})]}),_jsxs(Card,{title:`Dependency Vulnerability`,icon:`box`,children:[_jsxs(_components.p,{children:[`Blocks pull requests based on `,_jsx(_components.strong,{children:`vulnerable dependencies`}),` found by software composition analysis (SCA).`]}),_jsx(_components.p,{children:`Configure by:`}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Setting urgency/severity levels (Critical, High, Medium, Low)`}),`\n`,_jsx(_components.li,{children:`Or setting an inclusive CVSS score range from 0.0 to 10.0`}),`\n`,_jsxs(_components.li,{children:[`Optionally narrowing by `,_jsx(_components.a,{href:`#reachability`,children:`reachability`}),` (CI rules only)`]}),`\n`]}),_jsx(_components.p,{children:`Use this to prevent the introduction of packages with known security vulnerabilities, ensuring your supply chain remains secure.`})]}),_jsxs(Card,{title:`License Compliance`,icon:`file-contract`,children:[_jsx(_components.p,{children:`Blocks pull requests or CI pipelines when a dependency uses a denied license.`}),_jsx(_components.p,{children:`Configure by:`}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Selecting one or more license families: Copyleft, Permissive, or Commercial`}),`\n`,_jsxs(_components.li,{children:[`Entering specific SPDX license IDs, such as `,_jsx(_components.code,{children:`AGPL-3.0`})]}),`\n`]}),_jsx(_components.p,{children:`Use this to enforce your organization’s open-source and commercial license policy.`})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`how-it-works-with-github`,children:`How it Works with GitHub`}),`\n`,_jsx(Info,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Prerequisite`}),` You must have installed and configured the `,_jsx(_components.a,{href:`github`,children:`Corgea GitHub App`}),` with appropriate repository permissions.`]})}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Pull Request Submission`,children:_jsx(_components.p,{children:`Developer submits a pull request with code changes`})}),_jsx(Step,{title:`Automated Analysis`,children:_jsx(_components.p,{children:`System analyzes code changes against active blocking rules`})}),_jsxs(Step,{title:`Rule Validation`,children:[_jsx(_components.p,{children:`If violations are found, pull request is automatically blocked`}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=39013c8f8163f96d432b0f9bd4abbc05`,style:{borderRadius:`0.5rem`},\"data-og-width\":`2776`,width:`2776`,\"data-og-height\":`1034`,height:`1034`,\"data-path\":`images/blocking_rules_pr_blocked.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=a30829a8397256d24bf99e7714ff7e30 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=b52725944e1ae30ce07dba74e8a78478 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=e2e907951bbab46eafb1b64a6100d529 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=c14190cd9d640387e7fe0acef6794298 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=20a90628f1983af3321598d13d2379ce 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_blocked.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=e01f67509e07a92988339aeb7db7a652 2500w`})})]}),_jsxs(Step,{title:`Developer Notification`,children:[_jsx(_components.p,{children:`Developer receives detailed notification about rule violations`}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=4ac0e073341d12a425db9a4412e55b3e`,style:{borderRadius:`0.5rem`},\"data-og-width\":`3078`,width:`3078`,\"data-og-height\":`1834`,height:`1834`,\"data-path\":`images/blocking_rules_pr_details.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=993461300634968ea1133e1f1075f318 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=c26d7fbd66d8381ae4718b7ea7937556 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=8e23098e502c5bb6e23db507851b14d4 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=7fc794132c8af8c5aaaa5ba8568c32af 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=8614207f8ae7e8191e35f398b06b5d1f 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_pr_details.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=d53184a432c41abbf6718019d4b3315d 2500w`})})]}),_jsx(Step,{title:`Resolution`,children:_jsx(_components.p,{children:`Developer must fix violations and mark them as Fixed, or mark them as False Positive or Accepted Risk before merge is allowed`})})]}),`\n`,_jsx(Heading,{level:`2`,id:`how-it-works-with-azure-devops`,children:`How it Works with Azure DevOps`}),`\n`,_jsx(Info,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Prerequisite`}),` Make sure the `,_jsx(_components.a,{href:`azure_devops`,children:`Azure DevOps integration`}),` with Corgea is configured and you have the necessary permissions.`]})}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Pull Request Submission`,children:_jsx(_components.p,{children:`A developer submits a pull request with code changes in Azure DevOps.`})}),_jsx(Step,{title:`Automated Analysis`,children:_jsx(_components.p,{children:`The system evaluates the code changes against the active blocking rules set in Corgea.`})}),_jsxs(Step,{title:`Rule Validation`,children:[_jsx(_components.p,{children:`If violations are found, the pull request is automatically blocked.`}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=a85aa91d3cea8d9572197b863bafa4e4`,style:{borderRadius:`0.5rem`},\"data-og-width\":`966`,width:`966`,\"data-og-height\":`512`,height:`512`,\"data-path\":`images/azure_blocking_rules_pr_blocked.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=86916f9d80e1170fdac3a7a6581c11ed 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=1d9df77a9d453847fbbcde2404cb914c 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=0e07c663b2bd7279f941c7236fe8db5c 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=b195bcc896967e0a3af72fe6adf9bf08 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=d73a3cc8f4f2a5bcf17b500f2d33cada 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_blocking_rules_pr_blocked.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=b9b50b6d863396db4f51426e7c52e230 2500w`})}),_jsx(_components.p,{children:`Developer cannot merge the PR until it is resolved.`}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=1ecb01eb911476a19b0265a3b56dad72`,style:{borderRadius:`0.5rem`},\"data-og-width\":`2900`,width:`2900`,\"data-og-height\":`2630`,height:`2630`,\"data-path\":`images/azure-devops_merging_blocked.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=37a83ad08ba63540b6a96ded9fc2cded 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=f5abe6837c47c9a5301c45170b1cc4b2 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=af879f69a82cef36b02f696fd2567b2f 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=deff84406516ed9ad2994dbbc1008e3d 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=02811d94253b0fee59bffa0895e5ad6f 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure-devops_merging_blocked.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=3c2dfcc3cf1ee386008c1e32f8363064 2500w`})})]}),_jsxs(Step,{title:`Developer Notification`,children:[_jsx(_components.p,{children:`The developer receives a link to view detailed information about the failed issues on the Corgea Scan page.`}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=e5e94b8c2fec2b7abab7eb76a37533b1`,style:{borderRadius:`0.5rem`},\"data-og-width\":`2696`,width:`2696`,\"data-og-height\":`1556`,height:`1556`,\"data-path\":`images/azure_see_details_of_issues.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=b9e1574b516fa076e8dd9ea53b4ea330 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=02f81fbacf31ed9895533fc0769d1fbb 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=69bfc4d27b08d73c5b5390623f2a3199 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=da218b53310d9dc4bf4455e13c0b6a1f 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=694c295b80955a6b8023dfd6e153b8ab 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/azure_see_details_of_issues.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=c979dea0fc5967810d2feed2fe0c42ac 2500w`})})]}),_jsx(Step,{title:`Resolution`,children:_jsx(_components.p,{children:`The developer must resolve the violations by fixing them or marking them as False Positive or Accepted Risk before the merge can proceed.`})})]}),`\n`,_jsx(Heading,{level:`2`,id:`usage-guide`,children:`Usage Guide`}),`\n`,_jsx(Heading,{level:`3`,id:`creating-a-new-blocking-rule`,children:`Creating a New Blocking Rule`}),`\n`,_jsxs(Steps,{children:[_jsx(Step,{title:`Initiate Creation`,children:_jsx(_components.p,{children:`Click the “Add Blocking Rule” button`})}),_jsxs(Step,{title:`Choose Rule Type`,children:[_jsx(_components.p,{children:`Select the type of blocking rule:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Code Vulnerability`}),`: Block pull requests based on code security issues (SAST findings)`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Dependency Vulnerability`}),`: Block pull requests based on vulnerable dependencies (SCA findings)`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`License Compliance`}),`: Block dependencies based on denied SPDX licenses or license families`]}),`\n`]}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=8dcdba40b68a4f557b9af9b596629262`,style:{borderRadius:`0.5rem`},alt:`Add Blocking Rule modal with Applies To, rule types, and Issue Type`,\"data-og-width\":`459`,width:`459`,\"data-og-height\":`969`,height:`969`,\"data-path\":`images/blocking_rule_create.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?w=280\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=054d84d66c6f48f696d828c0efa94f28 280w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?w=560\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=c57934927acb0f211632bc15c5699d98 560w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?w=840\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=036c71d17df171e600be8149e3bae414 840w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?w=1100\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=155c38b31ee5862832c67fc3d14ca15e 1100w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?w=1650\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=e3aa6754cb1e3e51ed3aeb2676f6a962 1650w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create.png?w=2500\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=e9fdb9669593a43cb545adfd04f0e8dd 2500w`})})]}),_jsxs(Step,{title:`Basic Information`,children:[_jsxs(_components.p,{children:[`Enter the rule name and description, then choose `,_jsx(_components.strong,{children:`Applies To`}),`:`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Pull Requests`}),` automatically enforces the rule in pull request checks.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`CI`}),` enforces the rule only when a pipeline names it with `,_jsx(_components.code,{children:`corgea scan --block-on \u003cslug>`}),`. CI rules do not block pull requests.`]}),`\n`]}),_jsxs(_components.p,{children:[`New rules default to `,_jsx(_components.strong,{children:`Pull Requests`}),`. Corgea generates the slug from the rule name and displays it in the rules list.`]}),_jsx(_components.p,{children:`Pull request rules only comment on actionable findings. Corgea skips comments for findings confirmed as unreachable, findings held because they are false positives or unsupported-language results, and findings in paths ignored by the project. These findings remain available in Corgea for review, but they do not block the pull request.`}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=218cc233de7f4711f466cb92303eaf8c`,style:{borderRadius:`0.5rem`},alt:`Add Blocking Rule modal with CI selected and License Compliance configured`,\"data-og-width\":`469`,width:`469`,\"data-og-height\":`946`,height:`946`,\"data-path\":`images/blocking_rule_create_ci_license.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?w=280\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=bda2ae30611144e535eb3041ddf93fa7 280w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?w=560\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=0f5871ab6a6a37ba21752de25ee2bbf8 560w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?w=840\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=51fc5c2770cf781282b6bf209fae4f15 840w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?w=1100\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=4d3b6e80aceaf0eef8a619d78a543603 1100w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?w=1650\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=38a3cba1b960dff2533d5822af289b37 1650w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rule_create_ci_license.png?w=2500\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=dd1d7c2fbf0c19a69c5e131f4a9495cb 2500w`})})]}),_jsxs(Step,{title:`Configure Settings`,children:[_jsxs(_components.p,{children:[`For `,_jsx(_components.strong,{children:`Code Vulnerability`}),` rules: Choose an `,_jsx(_components.strong,{children:`Issue Type`}),` to apply the rule to `,_jsx(_components.strong,{children:`All`}),` findings, `,_jsx(_components.strong,{children:`Vulnerabilities`}),` only, or `,_jsx(_components.strong,{children:`Code Quality`}),` findings only. `,_jsx(_components.strong,{children:`All`}),` is the default and preserves the behavior of existing rules. Then select urgency levels (Critical, High, Medium, or Low) and/or target CWEs; at least one of these must be defined for the rule to be valid.`]}),_jsxs(_components.p,{children:[`For `,_jsx(_components.strong,{children:`Dependency Vulnerability`}),` rules: Choose whether to filter by severity or CVSS score. Select urgency levels (Critical, High, Medium, or Low), or enter a minimum and maximum CVSS score from 0.0 to 10.0 to block vulnerable dependencies within that inclusive range. If the rule applies to CI, you can also select one or more `,_jsx(_components.strong,{children:`Reachability`}),` states to narrow it further — see `,_jsx(_components.a,{href:`#reachability`,children:`Filtering by Reachability`}),`.`]}),_jsxs(_components.p,{children:[`For `,_jsx(_components.strong,{children:`License Compliance`}),` rules: Select at least one denied license family (Copyleft, Permissive, or Commercial) or enter one or more SPDX license IDs. A dependency is blocked when any reported license matches a selected family or specific ID.`]})]}),_jsx(Step,{title:`Set Scope`,children:_jsx(_components.p,{children:`Choose applicable projects and/or project tags (optional). A rule applies when a project is selected directly or has any selected tag. If no projects or tags are selected, the rule applies to all projects.`})}),_jsx(Step,{title:`Save`,children:_jsx(_components.p,{children:`Review and click “Create”`})})]}),`\n`,_jsx(Heading,{level:`3`,id:`managing-existing-rules`,children:`Managing Existing Rules`}),`\n`,_jsxs(_components.p,{children:[`Use search to find rules by name or settings, or filter the list by project tag or `,_jsx(_components.strong,{children:`Applies To`}),` target. The rules table shows each rule’s slug in the `,_jsx(_components.strong,{children:`ID`}),` column and surfaces the project scope, rule type, and `,_jsx(_components.strong,{children:`Pull Requests`}),` or `,_jsx(_components.strong,{children:`CI`}),` target under `,_jsx(_components.strong,{children:`Triggers On`}),`. Select a slug to copy it for use in a CI command. Rules without a project or tag scope apply to all projects, and longer scope lists are grouped behind a `,_jsx(_components.strong,{children:`+N more`}),` tooltip.`]}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=fde00215e97e017b81af0100480d9ad4`,style:{borderRadius:`0.5rem`},alt:`Blocking rules list showing slug, Triggers On chips, and CI badge`,\"data-og-width\":`1684`,width:`1684`,\"data-og-height\":`426`,height:`426`,\"data-path\":`images/blocking_rules_list.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?w=280\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=8c06df3c337c81f67933b5088b7e87ed 280w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?w=560\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=f8399245a6b352a83855e28215cb09ec 560w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?w=840\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=89883a75f698e720951a0d7b1b6f32d5 840w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?w=1100\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=7b06e9d7bb0079ffbeee0130091bca60 1100w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?w=1650\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=5b1eab64e860f6e34670f47dc121c539 1650w, https://mintcdn.com/corgea/vl87stO-uNzXPjoi/images/blocking_rules_list.png?w=2500\u0026fit=max\u0026auto=format\u0026n=vl87stO-uNzXPjoi\u0026q=85\u0026s=33c8434de4ae15c1aa2de026712993ea 2500w`})}),`\n`,_jsx(Heading,{level:`3`,id:`enforcing-rules-in-ci`,children:`Enforcing Rules in CI`}),`\n`,_jsxs(_components.p,{children:[`Create an active rule with `,_jsx(_components.strong,{children:`Applies To`}),` set to `,_jsx(_components.strong,{children:`CI`}),`, then pass its slug to the scan command. Name rules for the condition that trips them — for example `,_jsx(_components.code,{children:`criticals`}),`, not `,_jsx(_components.code,{children:`no-criticals`}),` — so `,_jsx(_components.code,{children:`--block-on`}),` reads as a direct assertion. `,_jsx(_components.code,{children:`--block-on`}),` requires Corgea CLI 1.10.0 or later.`]}),`\n`,_jsx(CodeBlock,{filename:``,numberOfLines:`1`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`1`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:`corgea`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` scan`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` --block-on`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` criticals`})]}),`\n`]})})}),`\n`,_jsxs(_components.p,{children:[`To enforce multiple CI rules, provide their slugs as a comma-separated list. The command fails when a finding violates any named rule. An unknown slug, inactive rule, or rule that applies to pull requests is treated as a configuration error rather than being skipped. `,_jsx(_components.code,{children:`--block-on`}),` is supported only by the BLAST scanner and cannot be combined with `,_jsx(_components.code,{children:`--fail`}),` or `,_jsx(_components.code,{children:`--fail-on`}),`.`]}),`\n`,_jsxs(Tabs,{children:[_jsx(Tab,{title:`Edit Rule`,id:`edit-rule`,children:_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`Locate rule in table`}),`\n`,_jsx(_components.li,{children:`Click “Edit” button`}),`\n`,_jsx(_components.li,{children:`Modify settings as needed`}),`\n`,_jsx(_components.li,{children:`Click “Update” to save`}),`\n`]})}),_jsx(Tab,{title:`Toggle Status`,id:`toggle-status`,children:_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`Find rule in table`}),`\n`,_jsx(_components.li,{children:`Click “Toggle Status”`}),`\n`,_jsx(_components.li,{children:`Confirm status change`}),`\n`]})}),_jsx(Tab,{title:`View Details`,id:`view-details`,children:_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`Click on rule name`}),`\n`,_jsx(_components.li,{children:`Review comprehensive information`}),`\n`,_jsx(_components.li,{children:`Close modal when done`}),`\n`]})})]}),`\n`,_jsx(Heading,{level:`3`,id:`viewing-rules-on-scans`,children:`Viewing Rules on scans`}),`\n`,_jsx(_components.p,{children:`You can view blocking rules that apply to your scans in two places:`}),`\n`,_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`On the scan details page, you’ll see a “Blocking Rules” section showing all rules that were evaluated:`}),`\n`]}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=a132f7927273e0eaf8bdb84065bbcbf4`,style:{borderRadius:`0.5rem`},\"data-og-width\":`1518`,width:`1518`,\"data-og-height\":`1082`,height:`1082`,\"data-path\":`images/blocking_rules_scan_details.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=2506f62e23926618d77b374cc6ce8af3 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=91aea5d0567b8909be5664ec94af61b5 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=c67566733fb8742f636ab401414ba9f7 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=1358301c8bdac7c1c0983a9276800f55 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=a6034b5277cd2545bae8dcdb914c793e 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rules_scan_details.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=4d1abeac5e45021533d8dbf10b0dd78b 2500w`})}),`\n`,_jsxs(_components.ol,{start:`2`,children:[`\n`,_jsx(_components.li,{children:`For individual issues, you can see which blocking rules were triggered in the issue details:`}),`\n`]}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=433dd74d99f714b953608a1e59ac973a`,style:{borderRadius:`0.5rem`},\"data-og-width\":`3072`,width:`3072`,\"data-og-height\":`1124`,height:`1124`,\"data-path\":`images/blocking_rule_issue_details.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?w=280\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=f018e1e8b4c4d92354a127e5716a8370 280w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?w=560\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=bda0c51d92e6a2caa2f3873e8eac83c3 560w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?w=840\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=e87b4d6f3d1cf506d64b64640d19c675 840w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?w=1100\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=7bd96c3f0fe932b1f8570a9c31539b93 1100w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?w=1650\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=f0d374fd9773f3a7e3c9def6a3ac77d1 1650w, https://mintcdn.com/corgea/uxLuQR4653lM43Tj/images/blocking_rule_issue_details.png?w=2500\u0026fit=max\u0026auto=format\u0026n=uxLuQR4653lM43Tj\u0026q=85\u0026s=3a59b8689328a1a8865b890a194cec4d 2500w`})}),`\n`,_jsx(_components.p,{children:`This makes it easy to understand which rules are affecting your scans and specific issues, helping you identify why certain changes may be blocked.`}),`\n`,_jsx(Heading,{level:`2`,id:`reachability`,children:`Filtering by Reachability`}),`\n`,_jsxs(_components.p,{children:[`Most vulnerable dependencies in a project are never actually exercised by your code. Reachability filtering lets a `,_jsx(_components.strong,{children:`Dependency Vulnerability`}),` rule block only the findings that matter, so a critical CVE in a package you never call does not fail your pipeline.`]}),`\n`,_jsx(Info,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Available for CI rules only`}),` Reachability is analyzed on scans you start yourself with `,_jsx(_components.code,{children:`corgea scan`}),`, not on the scans triggered automatically when a pull request opens. Set `,_jsx(_components.strong,{children:`Applies To`}),` to `,_jsx(_components.strong,{children:`CI`}),` to use this filter; the option is hidden for Pull Request rules, and reference the rule from your pipeline with `,_jsx(_components.code,{children:`corgea scan --block-on \u003cslug>`}),`.`]})}),`\n`,_jsx(Info,{children:_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Prerequisite`}),` Reachability requires `,_jsx(_components.strong,{children:`AI-Native SCA`}),` to be enabled for your organization. Without it no dependency is analyzed, so a rule using this filter never blocks anything. The rule editor warns you when the setting is off.`]})}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=571c043010e6323e09fc1523cfd8a5b3`,style:{borderRadius:`0.5rem`},alt:`Add Blocking Rule modal with CI and Dependency Vulnerability selected and Reachable checked under Reachability`,\"data-og-width\":`447`,width:`447`,\"data-og-height\":`884`,height:`884`,\"data-path\":`images/blocking_rule_create_ci_reachability.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?w=280\u0026fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=66a4ca8c20b9f1f1a54ed3a6814668b6 280w, https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?w=560\u0026fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=3a8b9ca58464b216ff030c6f0c47ae23 560w, https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?w=840\u0026fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=6cceeed7d4097b5ea18b37b3e5c3b15f 840w, https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?w=1100\u0026fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=e37a3d1e43b62043d3390608dfa36c44 1100w, https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?w=1650\u0026fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=d794c1e1d1a29b9ff2edcea67add2c28 1650w, https://mintcdn.com/corgea/gpJCGMHYx471xVvQ/images/blocking_rule_create_ci_reachability.png?w=2500\u0026fit=max\u0026auto=format\u0026n=gpJCGMHYx471xVvQ\u0026q=85\u0026s=c680e20859aaba7e1ccca3e8b8d632f5 2500w`})}),`\n`,_jsx(_components.p,{children:`Select one or more of the following states:`}),`\n`,_jsxs(Table,{children:[_jsx(_components.thead,{children:_jsxs(_components.tr,{children:[_jsx(_components.th,{children:`State`}),_jsx(_components.th,{children:`Meaning`})]})}),_jsxs(_components.tbody,{children:[_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Reachable`})}),_jsx(_components.td,{children:`The vulnerable function is reachable from your application code.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Not Reachable`})}),_jsx(_components.td,{children:`The dependency is used, but the vulnerable function is not reachable.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Unused Dependency`})}),_jsx(_components.td,{children:`The dependency is declared but not used anywhere in the codebase.`})]}),_jsxs(_components.tr,{children:[_jsx(_components.td,{children:_jsx(_components.strong,{children:`Unknown`})}),_jsx(_components.td,{children:`The dependency was analyzed but reachability could not be determined.`})]})]})]}),`\n`,_jsxs(_components.p,{children:[`The reachability filter is `,_jsx(_components.strong,{children:`combined with`}),` the severity, CVSS, or Malicious filter rather than replacing it, so a finding must match both. A rule set to Critical severity and Reachable blocks only critical vulnerabilities that are also reachable. Leaving reachability empty keeps the rule’s existing behavior of blocking regardless of reachability.`]}),`\n`,_jsx(Heading,{level:`3`,id:`waiting-for-analysis`,children:`Waiting for Analysis`}),`\n`,_jsxs(_components.p,{children:[`Reachability analysis runs after the scan itself completes, so `,_jsx(_components.code,{children:`corgea scan`}),` keeps polling while it finishes rather than reporting a result immediately. Analysis is done once every direct dependency has been analyzed, typically a few minutes and at most 30.`]}),`\n`,_jsxs(_components.p,{children:[`This filter `,_jsx(_components.strong,{children:`fails open`}),`. If analysis cannot finish — the 30-minute window elapses, analysis fails, or AI-Native SCA is disabled — the rule reports no violation instead of failing your build. A pipeline is only ever blocked on reachability that Corgea actually determined, never on missing analysis.`]}),`\n`,_jsxs(Warning,{children:[_jsxs(_components.p,{children:[_jsx(_components.code,{children:`corgea scan`}),` fails closed on its own deadline. Corgea CLI 1.13.0 and later allow 35 minutes, comfortably outlasting the 30-minute analysis window. On an earlier CLI the deadline is 15 minutes, which can expire while Corgea is still analyzing and fail the pipeline. Either upgrade the CLI or raise the deadline with `,_jsx(_components.code,{children:`CORGEA_BLOCKING_RULES_TIMEOUT_SECONDS`}),`:`]}),_jsx(CodeBlock,{filename:``,numberOfLines:`1`,language:`shellscript`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`shellscript`,children:_jsxs(_components.code,{language:`shellscript`,numberOfLines:`1`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#9CDCFE`},children:`CORGEA_BLOCKING_RULES_TIMEOUT_SECONDS`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`2100`}),_jsx(_components.span,{style:{color:`#953800`,\"--shiki-dark\":`#DCDCAA`},children:` corgea`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` scan`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#569CD6`},children:` --block-on`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` reachable-criticals`})]}),`\n`]})})})]}),`\n`,_jsx(Heading,{level:`2`,id:`examples`,children:`Examples`}),`\n`,_jsxs(AccordionGroup,{children:[_jsxs(Accordion,{title:`Blocking Insecure Cryptography`,icon:`lock`,id:`blocking-insecure-cryptography`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` Code Vulnerability`]}),_jsx(_components.p,{children:`Create a rule targeting CWE-326 (Inadequate Encryption Strength) and CWE-327 (Use of a Broken or Risky Cryptographic Algorithm) with “Critical” urgency to prevent weak encryption usage.`})]}),_jsxs(Accordion,{title:`Enforcing Code Quality`,icon:`code`,id:`enforcing-code-quality`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` Code Vulnerability`]}),_jsxs(_components.p,{children:[`Select `,_jsx(_components.strong,{children:`Code Quality`}),` as the issue type, then set up a rule for CWE-398 (Indicator of Poor Code Quality) and CWE-477 (Use of Obsolete Functions) with “Medium” urgency to maintain code standards.`]})]}),_jsxs(Accordion,{title:`Blocking Critical Dependency Vulnerabilities`,icon:`box`,id:`blocking-critical-dependency-vulnerabilities`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` Dependency Vulnerability`]}),_jsx(_components.p,{children:`Create a rule with “Critical” and “High” urgency levels selected to automatically block any pull request that introduces dependencies with critical or high-severity vulnerabilities. This ensures your supply chain remains secure and prevents known vulnerable packages from entering your codebase.`})]}),_jsxs(Accordion,{title:`Blocking Dependencies by CVSS Range`,icon:`gauge`,id:`blocking-dependencies-by-cvss-range`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` Dependency Vulnerability`]}),_jsx(_components.p,{children:`Create a rule that filters by CVSS score, such as 7.0 to 10.0, to block pull requests that introduce vulnerable dependencies within that score range.`})]}),_jsxs(Accordion,{title:`Blocking Only Reachable Critical Vulnerabilities`,icon:`diagram-project`,id:`blocking-only-reachable-critical-vulnerabilities`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` Dependency Vulnerability — `,_jsx(_components.strong,{children:`Applies To:`}),` CI`]}),_jsxs(_components.p,{children:[`Select “Critical” and “High” urgency levels, then select `,_jsx(_components.strong,{children:`Reachable`}),` under Reachability. The rule fails a pipeline only when a critical or high-severity vulnerability is reachable from your application code, so unused and unreachable packages do not interrupt developers. This is a good first reachability rule because it narrows an existing severity rule rather than widening what blocks.`]})]}),_jsxs(Accordion,{title:`Blocking Unused Dependencies`,icon:`broom`,id:`blocking-unused-dependencies`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` Dependency Vulnerability — `,_jsx(_components.strong,{children:`Applies To:`}),` CI`]}),_jsxs(_components.p,{children:[`Select `,_jsx(_components.strong,{children:`Unused Dependency`}),` under Reachability on its own, with no severity or CVSS filter. The rule fails a pipeline that introduces vulnerable packages nothing in the codebase uses, prompting developers to remove the dependency instead of upgrading it.`]})]}),_jsxs(Accordion,{title:`Blocking Copyleft Dependencies`,icon:`file-contract`,id:`blocking-copyleft-dependencies`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Rule Type:`}),` License Compliance`]}),_jsxs(_components.p,{children:[`Select the `,_jsx(_components.strong,{children:`Copyleft`}),` family to block dependencies whose reported licenses belong to that family. Add specific SPDX IDs when your policy needs a narrower denylist.`]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`best-practices`,children:`Best Practices`}),`\n`,_jsx(Card,{title:`Implementation Tips`,icon:`lightbulb`,children:_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Start with essential rules and gradually expand`}),`\n`,_jsxs(_components.li,{children:[`For `,_jsx(_components.strong,{children:`Dependency Vulnerability rules`}),`, begin with Critical severity only or a focused CVSS range, then expand as your team adjusts`]}),`\n`,_jsxs(_components.li,{children:[`On `,_jsx(_components.strong,{children:`CI rules`}),`, add a `,_jsx(_components.strong,{children:`Reachable`}),` reachability filter to an existing severity rule to cut noise without weakening coverage of the vulnerabilities that are actually exploitable`]}),`\n`,_jsxs(_components.li,{children:[`For `,_jsx(_components.strong,{children:`Code Vulnerability rules`}),`, focus on the most impactful CWEs first (e.g., injection flaws, authentication issues)`]}),`\n`,_jsx(_components.li,{children:`Regular review and updates`}),`\n`,_jsx(_components.li,{children:`Clear documentation and team training`}),`\n`,_jsx(_components.li,{children:`Encourage feedback and collaboration`}),`\n`,_jsx(_components.li,{children:`Strategic use of urgency levels`}),`\n`,_jsx(_components.li,{children:`Consider project tags when the same rule should cover a group of related projects`}),`\n`]})}),`\n`,_jsx(Heading,{level:`2`,id:`troubleshooting`,children:`Troubleshooting`}),`\n`,_jsx(Warning,{children:`If a pull request is unexpectedly blocked, verify the active rules and their configurations first.`}),`\n`,_jsxs(AccordionGroup,{children:[_jsx(Accordion,{title:`Common Issues`,icon:`bug`,id:`common-issues`,children:_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Unexpected blocking behavior`}),`\n`,_jsx(_components.li,{children:`Rule targeting issues`}),`\n`,_jsx(_components.li,{children:`Project scope problems`}),`\n`]})}),_jsx(Accordion,{title:`Resolution Steps`,icon:`wrench`,id:`resolution-steps`,children:_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Check rule configurations`}),`\n`,_jsx(_components.li,{children:`Verify CWE targeting`}),`\n`,_jsx(_components.li,{children:`Confirm project settings`}),`\n`,_jsx(_components.li,{children:`Contact support if needed`}),`\n`]})})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"Blocking Rules","description":"Blocking rules enforce security and quality standards in pull requests or CI pipelines.","href":"/blocking_rules"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"Overview","slug":"overview","depth":2,"children":[{"title":"What it Does","slug":"what-it-does","depth":3,"children":[]},{"title":"Who it’s For","slug":"who-it’s-for","depth":3,"children":[]}]},{"title":"Key Features and Benefits","slug":"key-features-and-benefits","depth":2,"children":[]},{"title":"Rule Types","slug":"rule-types","depth":2,"children":[]},{"title":"How it Works with GitHub","slug":"how-it-works-with-github","depth":2,"children":[]},{"title":"How it Works with Azure DevOps","slug":"how-it-works-with-azure-devops","depth":2,"children":[]},{"title":"Usage Guide","slug":"usage-guide","depth":2,"children":[{"title":"Creating a New Blocking Rule","slug":"creating-a-new-blocking-rule","depth":3,"children":[]},{"title":"Managing Existing Rules","slug":"managing-existing-rules","depth":3,"children":[]},{"title":"Enforcing Rules in CI","slug":"enforcing-rules-in-ci","depth":3,"children":[]},{"title":"Viewing Rules on scans","slug":"viewing-rules-on-scans","depth":3,"children":[]}]},{"title":"Filtering by Reachability","slug":"reachability","depth":2,"children":[{"title":"Waiting for Analysis","slug":"waiting-for-analysis","depth":3,"children":[]}]},{"title":"Examples","slug":"examples","depth":2,"children":[]},{"title":"Best Practices","slug":"best-practices","depth":2,"children":[]},{"title":"Troubleshooting","slug":"troubleshooting","depth":2,"children":[]}],"codeExamples":{}},"jsLinks":[],"subdomain":"corgea","siteName":"Corgea Documentation","title":"Blocking Rules - Corgea Documentation","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{"en":{"href":"/blocking_rules","matchLevel":0},"de":{"href":"/de/blocking_rules","matchLevel":1},"fr":{"href":"/fr/blocking_rules","matchLevel":1},"es":{"href":"/es/blocking_rules","matchLevel":1},"ja":{"href":"/ja/blocking_rules","matchLevel":1}}},"lastModified":"2026-09-07T17:47:53.575Z","originalFileLocation":"blocking_rules.mdx","locale":"en"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Blocking rules enforce security and quality standards in pull requests or CI pipelines.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Corgea Documentation\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Blocking Rules - Corgea Documentation\">\u003cmeta data-mint-head property=\"og:description\" content=\"Blocking rules enforce security and quality standards in pull requests or CI pipelines.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Corgea Documentation\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://docs.corgea.app/blocking_rules\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://corgea.mintlify.app/_mintlify/api/og/v2?division=Policy+Management\u0026amp;title=Blocking+Rules\u0026amp;description=Blocking+rules+enforce+security+and+quality+standards+in+pull+requests+or+CI+pipelines.\u0026amp;theme=41074bc9e80898ad3ff58073\u0026amp;signature=150b1b38c50ed9898ac1bc5bdf71b2a30f8077d872c4b8ae5ca8a60603a5dd89\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Blocking Rules - Corgea Documentation\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Blocking rules enforce security and quality standards in pull requests or CI pipelines.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://corgea.mintlify.app/_mintlify/api/og/v2?division=Policy+Management\u0026amp;title=Blocking+Rules\u0026amp;description=Blocking+rules+enforce+security+and+quality+standards+in+pull+requests+or+CI+pipelines.\u0026amp;theme=41074bc9e80898ad3ff58073\u0026amp;signature=150b1b38c50ed9898ac1bc5bdf71b2a30f8077d872c4b8ae5ca8a60603a5dd89\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/mintlify-assets/_mintlify/favicons/corgea/S1IZmkPVVuf-3VMn/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Corgea Documentation\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#F56C26\">\u003clink data-mint-head rel=\"canonical\" href=\"https://docs.corgea.app/blocking_rules\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/blocking_rules.md\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"en\" href=\"https://docs.corgea.app/blocking_rules\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"de\" href=\"https://docs.corgea.app/de/blocking_rules\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"fr\" href=\"https://docs.corgea.app/fr/blocking_rules\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"es\" href=\"https://docs.corgea.app/es/blocking_rules\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"ja\" href=\"https://docs.corgea.app/ja/blocking_rules\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"x-default\" href=\"https://docs.corgea.app/blocking_rules\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://docs.corgea.app/#organization\",\"name\":\"Corgea Documentation\",\"url\":\"https://docs.corgea.app\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/corgea/mpJUc1GyXtnVYEyT/logo/logo.png?fit=max\u0026auto=format\u0026n=mpJUc1GyXtnVYEyT\u0026q=85\u0026s=f66a9484335ac4db5d5d92e12fd87af6\"}},{\"@type\":\"WebSite\",\"@id\":\"https://docs.corgea.app#website\",\"name\":\"Corgea Documentation\",\"url\":\"https://docs.corgea.app\",\"publisher\":{\"@id\":\"https://docs.corgea.app/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://docs.corgea.app/blocking_rules#webpage\",\"url\":\"https://docs.corgea.app/blocking_rules\",\"name\":\"Blocking Rules\",\"description\":\"Blocking rules enforce security and quality standards in pull requests or CI pipelines.\",\"dateModified\":\"2026-09-07T17:47:53.575Z\",\"isPartOf\":{\"@id\":\"https://docs.corgea.app#website\"},\"breadcrumb\":{\"@id\":\"https://docs.corgea.app/blocking_rules#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://docs.corgea.app/blocking_rules#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Core Features\",\"item\":\"https://docs.corgea.app/agent\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Policy Management\",\"item\":\"https://docs.corgea.app/policies\"},{\"@type\":\"ListItem\",\"position\":3,\"name\":\"Blocking Rules\",\"item\":\"https://docs.corgea.app/blocking_rules\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://docs.corgea.app/blocking_rules#article\",\"headline\":\"Blocking Rules\",\"name\":\"Blocking Rules\",\"description\":\"Blocking rules enforce security and quality standards in pull requests or CI pipelines.\",\"url\":\"https://docs.corgea.app/blocking_rules\",\"mainEntityOfPage\":{\"@id\":\"https://docs.corgea.app/blocking_rules#webpage\"},\"dateModified\":\"2026-09-07T17:47:53.575Z\",\"publisher\":{\"@id\":\"https://docs.corgea.app/#organization\"},\"isPartOf\":{\"@id\":\"https://docs.corgea.app#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Corgea Documentation\",\"creator\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","siteName":"Corgea Documentation","nav":{"global":null,"languages":[{"language":"en","default":true,"navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Support"}],"primary":{"type":"button","label":"Go to Corgea","href":"https://www.corgea.app"}},"anchors":[{"anchor":"Documentation","icon":"book-open","groups":[{"group":"Getting Started","pages":[{"title":"Corgea Documentation","sidebarTitle":"Introduction","mode":"wide","href":"/introduction"},{"title":"Quickstart","href":"/quickstart"},{"title":"Settings","href":"/settings"}]},{"group":"Core Features","pages":[{"title":"Corgea Agent","href":"/agent"},{"title":"Security Design Reviews","href":"/security-review"},{"title":"Code Quality","href":"/code-quality-scanner"},{"title":"Pentesting","href":"/pentesting"},{"group":"Security Scanning","pages":[{"title":"AI-native SAST","href":"/blast"},{"title":"Secret Scanning","href":"/secret-scanning"},{"title":"Dependency Scanning (SCA)","href":"/sca"},{"title":"Container Image Scanning","href":"/container-scanning"},{"title":"Malicious Package Detection","href":"/malware-scanning"},{"title":"PII/PHI Scanning","href":"/pii"},{"title":"Infrastructure as Code (IaC) Scanning","href":"/iac"},{"title":"Uploading Scans","href":"/upload-report"},{"title":"Scheduled Scans","href":"/scheduled-scans"},{"title":"Issue Fingerprinting","href":"/fingerprint"}]},{"group":"Issue Management","pages":[{"title":"Vulnerabilities Workbench","href":"/vulnerabilities"},{"title":"Applying Fixes","href":"/fixes"},{"title":"False Positive Detection","href":"/false_positive"},{"title":"Issue Assignment \u0026 Status Management","href":"/issue_assignment"},{"title":"Triage Justifications","href":"/triage_justifications"},{"title":"Issue Export","href":"/issue_export"},{"title":"Project Management","href":"/project"}]},{"group":"Policy Management","pages":[{"title":"PolicyIQ","href":"/policies"},{"title":"SLA Management","description":"Configure and manage Service Level Agreements (SLAs) for security issues","href":"/sla_management"},{"title":"Blocking Rules","href":"/blocking_rules"}]},{"group":"Users \u0026 Groups","pages":[{"title":"User Management","description":"Manage your users in Corgea","href":"/user_management"},{"title":"Roles","href":"/permission_groups"},{"title":"Teams","href":"/teams"},{"title":"Content Access Management","href":"/content-access-management"},{"title":"Notifications","href":"/notifications"}]},{"title":"Reporting","href":"/reporting"}]},{"group":"Integrations","pages":[{"group":"IDEs","pages":[{"title":"Visual Studio Code and Cursor","sidebarTitle":"VS Code and Cursor","href":"/vsc_extension"},{"title":"Visual Studio 2022","href":"/vs2022_extension"},{"title":"JetBrains IDEs","href":"/jetbrains_extension"}]},{"group":"Source Control","pages":[{"title":"GitHub","href":"/github"},{"title":"GitLab","href":"/gitlab"},{"title":"Azure DevOps","href":"/azure_devops"},{"title":"Bitbucket","href":"/bitbucket"},{"title":"Harness","href":"/harness"}]},{"group":"Automation Management","pages":[{"title":"JIRA","href":"/jira"},{"title":"Linear","href":"/linear"},{"title":"Slack","href":"/slack"},{"title":"Zapier","href":"/zapier"},{"title":"Webhooks","href":"/webhooks"}]},{"title":"Private Package Registries","href":"/private-package-registries"},{"title":"Agentic Integrations","href":"/agentic_integrations"}]},{"group":"Tools \u0026 Utilities","pages":[{"group":"CLI","pages":[{"title":"CLI","href":"/cli"},{"title":"Dependency Scanning (CLI)","href":"/cli/deps"}]},{"title":"Model Context Protocol (MCP)","href":"/modelcontextprotocol"}]},{"group":"Releases","pages":[{"title":"Changelog","href":"/changelog"}]},{"group":"Trust \u0026 Compliance","pages":[{"title":"Security","href":"/security"},{"title":"Vulnerability Disclosure Policy","href":"/vulnerability-disclosure"},{"title":"Legal","href":"/legal"}]},{"group":"Authentication","pages":[{"title":"SSO","href":"/sso"},{"title":"JWT Auth","href":"/jwt-token"}]}]},{"anchor":"Service Status","icon":"check","href":"https://status.corgea.app/"},{"anchor":"Blog","icon":"newspaper","href":"https://corgea.com/blog"},{"anchor":"API Reference","icon":"square-terminal","pages":[{"title":"API Reference","href":"/api-reference/introduction"}]}]},{"language":"de","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Support"}],"primary":{"type":"button","label":"Zu Corgea","href":"https://www.corgea.app"}},"pages":[{"title":"de","href":"/de/blocking_rules"}]},{"language":"fr","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Assistance"}],"primary":{"type":"button","label":"Accéder à Corgea","href":"https://www.corgea.app"}},"pages":[{"title":"fr","href":"/fr/blocking_rules"}]},{"language":"es","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"Soporte"}],"primary":{"type":"button","label":"Ir a Corgea","href":"https://www.corgea.app"}},"pages":[{"title":"es","href":"/es/blocking_rules"}]},{"language":"ja","navbar":{"links":[{"href":"mailto:help@corgea.com","label":"サポート"}],"primary":{"type":"button","label":"Corgeaを開く","href":"https://www.corgea.app"}},"pages":[{"title":"ja","href":"/ja/blocking_rules"}]}]},"basePath":"","title":"Blocking Rules - Corgea Documentation","buildId":"dpl_DeHjVRGfFnhYQwHnfC2pjeXXv8h9","deploymentId":"dpl_DeHjVRGfFnhYQwHnfC2pjeXXv8h9","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-DXXFP6nH.js","DynamicMarkdown-B54_zNBF.js","zoom-image-lightbox-BG6oD64b.js","lightbox-handle-r17bVUz3.js"]}