> ## Documentation Index
> Fetch the complete documentation index at: https://docs.corgea.app/llms.txt
> Use this file to discover all available pages before exploring further.
# Roles
> This document provides a comprehensive overview of all permissions available for assignment to roles in the Corgea platform. Permissions control what actions users can perform within the system.
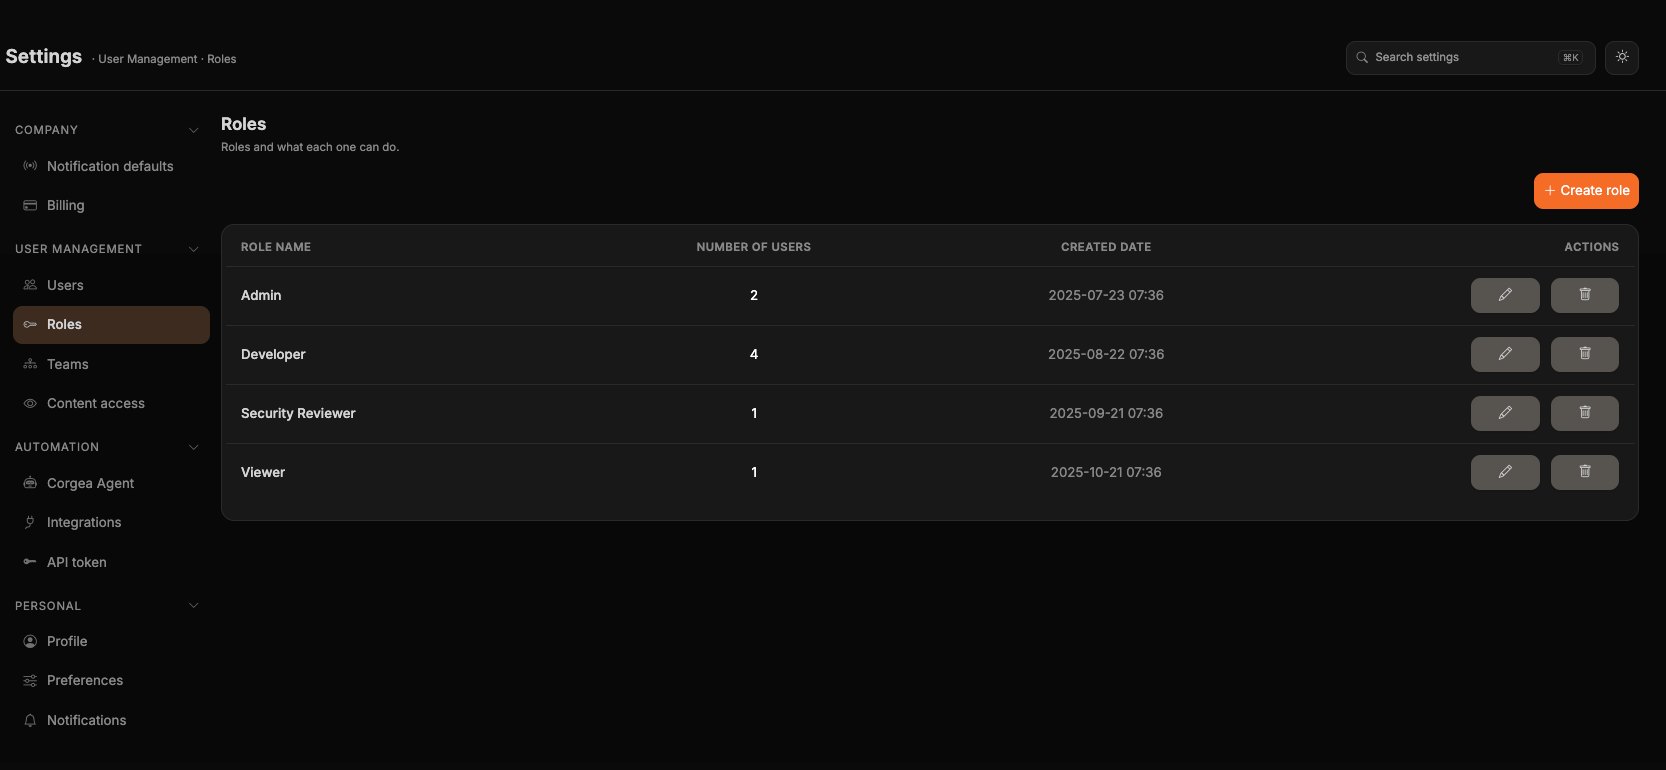
Manage roles at **Settings → User Management → [Roles](https://www.corgea.app/settings/company/groups/)**. Viewing this page requires the **Can view Permission Group** permission and a plan that includes role management.
 ## What are Role-Based Permissions?
Role-based permissions (also known as Role-Based Access Control or RBAC) is a security model that restricts system access based on a user's role within an organization. Instead of assigning permissions to individual users, permissions are assigned to roles, and users are then assigned to appropriate roles based on their job functions.
### Key Benefits
* **Simplified Management**: Assign permissions once to a role, then add users to that role rather than managing permissions for each individual user
* **Consistency**: Ensures all users with the same role have identical access rights
* **Scalability**: Easy to onboard new team members by assigning them to pre-configured roles
* **Security**: Follows the principle of least privilege by granting only the permissions necessary for each role
* **Audit & Compliance**: Simplifies access reviews and compliance reporting by organizing permissions around job functions
### How It Works in Corgea
In Corgea, you create **roles** that correspond to job functions in your organization (e.g., Admin, Developer, Security Manager). Each role is assigned a specific set of permissions that define what actions those users can perform. Users are then added to one or more roles, inheriting all permissions from those roles.
Permissions are **additive** - if a user belongs to multiple roles, they receive all permissions from all roles they are a member of.
## Role-Based Permission Recommendations
Based on the permissions defined in the Corgea platform, here's a recommended permission matrix for different roles.
### Role Descriptions
Full system access - can manage all aspects of the platform including company settings, users, permissions, and all security features.
Can manage development teams, users, projects, and view all security issues. Can initiate scans and manage team assignments but cannot modify security policies.
Read access to issues, scans, policies, and teams. Can initiate scans for their projects but has limited management capabilities. Focus on viewing and understanding security issues in their code.
Operational focus with full control over integrations, scheduled scans, agent settings, and PR automation rules. Can manage scans and view issues but cannot modify security policies or delete issues.
Comprehensive security management including all policy controls, SLAs, blocking rules, and user/team management. Cannot delete roles or modify company settings.
Hands-on security role with full control over security issues, policies, scans, and agent settings. Focus on day-to-day security operations but without user/team management responsibilities.
### Roles Overview
The following are suggested roles to set up. Corgea comes with the Admin role out of the box.
| Permission | Admin (Default) | Security Manager | Security Engineer | Development Manager | Developer | DevOps |
| - | :-: | :-: | :-: | :-: | :-: | :-: |
| **User Management** | | | | | | |
| Create User | ✓ | ✓ | ✗ | ✗ | ✗ | ✗ |
| Edit User | ✓ | ✓ | ✗ | ✗ | ✗ | ✗ |
| Delete User | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| View User | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| **Issue Management (SAST)** | | | | | | |
| Create Issue | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| View Issue | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Delete Issue | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| **SCA Issue Management** | | | | | | |
| Create SCA Issue | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| View SCA Issue | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Edit SCA Issue | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| Delete SCA Issue | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| **SAST Scan Management** | | | | | | |
| Create SAST Scan | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| View SAST Scan | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Delete SAST Scan | ✓ | ✓ | ✓ | ✓ | ✗ | ✓ |
| **Project Management** | | | | | | |
| Modify Project Tags | ✓ | ✓ | ✗ | ✓ | ✗ | ✓ |
| Edit Project | ✓ | ✓ | ✗ | ✓ | ✗ | ✓ |
| Delete Project | ✓ | ✗ | ✗ | ✓ | ✗ | ✗ |
| **API Token Management** | | | | | | |
| View API Token | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Manage API Token | ✓ | ✓ | ✗ | ✗ | ✗ | ✓ |
| **Policy Management** | | | | | | |
| Create Policy | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| Edit Policy | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| View Policy | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Delete Policy | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| **Issue SLA Management** | | | | | | |
| Create Issue SLA | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| Edit Issue SLA | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| View Issue SLA | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Delete Issue SLA | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| **Blocking Rule Management** | | | | | | |
| Create Blocking Rule | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| Edit Blocking Rule | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| View Blocking Rule | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Delete Blocking Rule | ✓ | ✓ | ✓ | ✗ | ✗ | ✗ |
| **PR Scan & Comment Rules** | | | | | | |
| Create PR Scan & Comment Rule | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| Edit PR Scan & Comment Rule | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| View PR Scan & Comment Rule | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Delete PR Scan & Comment Rule | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| **Scheduled Scan Management** | | | | | | |
| Create Scheduled Scan | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| Edit Scheduled Scan | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| View Scheduled Scan | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| Delete Scheduled Scan | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| **Integration Management** | | | | | | |
| View Integration | ✓ | ✓ | ✓ | ✓ | ✗ | ✓ |
| Manage Integration | ✓ | ✓ | ✗ | ✗ | ✗ | ✓ |
| **Role Management** | | | | | | |
| Create Role | ✓ | ✓ | ✗ | ✗ | ✗ | ✗ |
| Edit Role | ✓ | ✓ | ✗ | ✗ | ✗ | ✗ |
| View Role | ✓ | ✓ | ✗ | ✓ | ✗ | ✗ |
| Delete Role | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| **Company Management** | | | | | | |
| View Company Settings | ✓ | ✓ | ✗ | ✓ | ✗ | ✓ |
| Edit Company Settings | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| **Corgea Agent Settings** | | | | | | |
| View Agent Settings | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| Edit Agent Settings | ✓ | ✓ | ✓ | ✗ | ✗ | ✓ |
| **Skills Registry** | | | | | | |
| Create Skill | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Edit Skill | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| View Skill | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Delete Skill | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| Approve Skill | ✓ | ✗ | ✗ | ✗ | ✗ | ✗ |
| **Team Management** | | | | | | |
| View Team | ✓ | ✓ | ✓ | ✓ | ✓ | ✓ |
| Create Team | ✓ | ✓ | ✗ | ✓ | ✗ | ✗ |
| Edit Team | ✓ | ✓ | ✗ | ✓ | ✗ | ✗ |
| Delete Team | ✓ | ✗ | ✗ | ✓ | ✗ | ✗ |
| **Content Access Management** | | | | | | |
| Manage Content Access | ✓ | ✓ | ✗ | ✓ | ✗ | ✗ |
## Best Practices
Determine the specific roles and responsibilities within your organization (e.g., Security Analyst, Developer, Manager).
Assign only the minimum required permissions for each role to follow the principle of least privilege.
Create roles that correspond to organizational job functions and assign the appropriate permissions.
Add users to the appropriate roles based on their job function and responsibilities.
Regularly audit permission assignments to ensure they align with current organizational needs
Remove unused permissions and clean up deprecated roles
Use integration user permissions only for automated systems, not human users
Implement regular reviews of high-privilege permissions like user management and policy changes
If a user cannot perform an expected action, check their role assignments and individual permissions
Use the view permissions to audit what access a user or role currently has
Remember that permissions are additive - users get all permissions from all roles they belong to
## Permissions Reference
Below is a complete reference of all available permissions in the Corgea platform with their descriptions and use cases.
### User Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add user** | Create new user accounts in the system | Register new team members and set up their accounts |
| **Can change user** | Modify existing user account information and settings | Update user profiles, change email addresses, modify user roles, or update account details |
| **Can delete user** | Remove user accounts from the system | Deactivate or permanently delete user accounts when team members leave or accounts are no longer needed |
| **Can view user** | View user account information and profiles | Access user details, view team member information, or check user status |
### Issue Management Permissions (SAST)
| Permission | Description | Use Case |
| - | - | - |
| **Can add issue** | Create new security issues or manually report vulnerabilities | Allow security team members to manually create issues for discovered vulnerabilities or security concerns |
| **Can view issue** | View security issues, vulnerabilities, and their details | Access issue reports, review vulnerability details, or monitor security status across projects |
| **Can delete issue** | Remove security issues from the system | Clean up false positives, remove resolved issues, or manage issue lifecycle |
| **Can approve or reject triage requests** | Review another user's pending false-positive or accepted-risk requests | Approve or reject triage decisions for finding types the reviewer can change |
### SCA Issue Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add sca issue** | Create new SCA issues or manually report dependency vulnerabilities | Manually flag dependency issues, report newly discovered vulnerabilities in third-party components |
| **Can view sca issue** | View Software Composition Analysis issues and dependency vulnerabilities | Review third-party library vulnerabilities, check dependency security status, or analyze open source component risks |
| **Can change sca issue** | Modify SCA issue details, status, or resolution information | Update issue status, add resolution notes, or modify vulnerability assessment details |
| **Can delete sca issue** | Remove SCA issues from the system | Clean up false positives, remove resolved dependency issues, or manage SCA issue lifecycle |
### SAST Scan Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add SAST Scan** | Initiate new SAST security scans on projects | Start security scans, trigger manual scans, or schedule new security analysis runs |
| **Can view SAST Scan** | View SAST scan results, reports, and scan history | Review scan results, analyze security findings, or monitor scan progress and outcomes |
| **Can delete SAST Scan** | Remove SAST scan records and results from the system | Clean up old scan data, remove failed scans, or manage scan history storage |
### Project Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can modify project tags** | Add, remove, or modify tags associated with projects | Organize projects with custom tags, categorize projects by team or technology, or improve project management and filtering |
| **Can edit project** | Modify project settings and configuration | Update project details, change project settings, or adjust project parameters |
| **Can delete project** | Remove projects from the system (requires project access when Project Access Control is enabled) | Clean up old projects, remove deprecated projects, or manage project lifecycle |
### API Token Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can view token** | View API tokens and their associated permissions and usage | Review token usage, audit API access, or check token permissions and status |
| **Can change token** | Modify API tokens, including regeneration, expiration, or permission changes | Update token permissions, regenerate compromised tokens, or modify token expiration settings |
### Policy Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add Policy** | Create new security policies and compliance rules | Define new security standards, create compliance policies, or establish organizational security guidelines |
| **Can change Policy** | Modify existing policies, rules, and compliance settings | Update policy requirements, adjust compliance rules, or modify security standards as organizational needs change |
| **Can view Policy** | View policies, compliance rules, and security standards | Review current policies, understand compliance requirements, or audit security standards |
| **Can delete Policy** | Remove policies and compliance rules from the system | Clean up outdated policies, remove deprecated compliance rules, or manage policy lifecycle |
### Issue SLA Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add Issue SLA** | Create new issue SLA definitions and response time requirements | Define response time requirements for different types of security issues, set up escalation procedures |
| **Can change Issue SLA** | Modify existing issue SLA settings and response time requirements | Update SLA requirements, adjust response times, or modify escalation procedures |
| **Can view Issue SLA** | View issue SLA settings and response time requirements | Review SLA requirements, check response time commitments, or audit SLA compliance |
| **Can delete Issue SLA** | Remove issue SLA definitions from the system | Clean up outdated SLA requirements or remove deprecated response time standards |
### Blocking Rule Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add blocking rule** | Create new blocking rules to prevent specific actions or deployments | Set up rules to block deployments with critical vulnerabilities, prevent releases with compliance violations |
| **Can change blocking rule** | Modify existing blocking rules and their conditions | Update blocking criteria, adjust rule conditions, or modify deployment restrictions |
| **Can view blocking rule** | View blocking rules and their current configurations | Review current blocking rules, understand deployment restrictions, or audit rule effectiveness |
| **Can delete blocking rule** | Remove blocking rules from the system | Clean up outdated rules, remove unnecessary restrictions, or manage rule lifecycle |
### PR Scan Comment Rule Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add pr scan comment rule** | Create new rules for automated comments on pull request scans | Set up automated feedback for developers, create custom comment templates for different scan results |
| **Can change pr scan comment rule** | Modify existing PR scan comment rules and templates | Update comment templates, adjust feedback rules, or modify automated communication settings |
| **Can view pr scan comment rule** | View PR scan comment rules and their configurations | Review current comment rules, understand automated feedback settings, or audit communication policies |
| **Can delete pr scan comment rule** | Remove PR scan comment rules from the system | Clean up outdated comment rules, remove unnecessary automated feedback, or manage rule lifecycle |
### Scheduled Scan Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add Scheduled Scan** | Create new scheduled security scans with custom timing and parameters | Set up regular security scans, create automated scan schedules, or establish recurring security assessments |
| **Can change Scheduled Scan** | Modify existing scheduled scan settings, timing, or parameters | Update scan frequency, adjust scan parameters, or modify scheduling configurations |
| **Can view Scheduled Scan** | View scheduled scan configurations and their current settings | Review scan schedules, check upcoming scans, or audit automated scanning configurations |
| **Can delete Scheduled Scan** | Remove scheduled scans from the system | Clean up outdated scan schedules, remove unnecessary automated scans, or manage scan lifecycle |
### Integration Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can view integration** | View integration configurations and connection details | Review current integrations, check integration status, or audit external connections |
| **Can manage integration** | Create, modify, and configure integrations with external systems | Set up new integrations, update integration settings, or manage external system connections |
### Role Management Permissions
These permissions appear in the app as **Can add/change/view/delete Permission Group**. They control who can manage roles.
| Permission | Description | Use Case |
| - | - | - |
| **Can add Permission Group** | Create new roles with custom permission sets | Set up role-based access control by creating roles like "Developers", "Security Team", or "Managers" with specific permissions |
| **Can change Permission Group** | Modify existing role settings and assigned permissions | Update role permissions, change role names, or adjust access levels as organizational needs evolve |
| **Can view Permission Group** | View role configurations and assigned permissions | Review current role settings, audit permissions, or understand the access control structure |
| **Can delete Permission Group** | Remove roles from the system | Clean up unused roles or remove deprecated role configurations |
### Company Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can view company** | View company information, settings, and billing usage | Access company details, review organizational information, or check company-wide settings, policies, and billing limits |
| **Can change company** | Modify company settings, billing, configuration, and organizational details | Update company information, manage billing settings, modify organizational policies, or adjust company-wide configurations |
### Corgea Agent Settings Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can view agent settings** | View Corgea Agent configuration and settings | Review agent configurations, check agent status, or audit agent settings |
| **Can edit agent settings** | Modify Corgea Agent configuration and settings | Update agent parameters, change agent behavior, or adjust automation settings |
### Skills Registry Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can add skill** | Create new skills in the Skills Registry | Author company skills and submit their initial versions for review |
| **Can change skill** | Modify skills and submit new skill versions | Update skill instructions, publish a new version, or resubmit after review feedback |
| **Can view skill** | View skills, versions, review status, and installability | Browse available skills, inspect version history, and check whether a skill is approved for installation |
| **Can delete skill** | Remove skills from the registry | Retire outdated or unwanted skills from the organization |
| **Can approve skill** | Approve or reject skill versions | Complete a skill version review before it becomes installable |
### Team Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can view team** | View team information, members, and assignments | Access team details, review team composition, or check team assignments |
| **Can create team** | Create new teams within the organization | Set up new development teams, security teams, or organizational units |
| **Can edit team** | Modify team information, members, and assignments | Update team details, add or remove team members, or adjust team configurations |
| **Can delete team** | Remove teams from the system | Clean up disbanded teams, remove deprecated organizational units, or manage team lifecycle |
### Content Access Management Permissions
| Permission | Description | Use Case |
| - | - | - |
| **Can manage content access** | Control access to content and resources within the platform | Define who can access specific projects, repositories, or security data; manage content visibility and access controls |
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.